Kuzular anneleri ile buluştu, o anlar dron kamerasıyla görüntülendi
Kars’ın Arpaçay ilçesinde, Mehmet Özkaya’ya ait çiftlikte koyunlar ve kuzuları ilk kez buluştu. Dron kamerasıyla kaydedilen bu anlar, çiftliğin doğal yaşamını gözler önüne serdi.

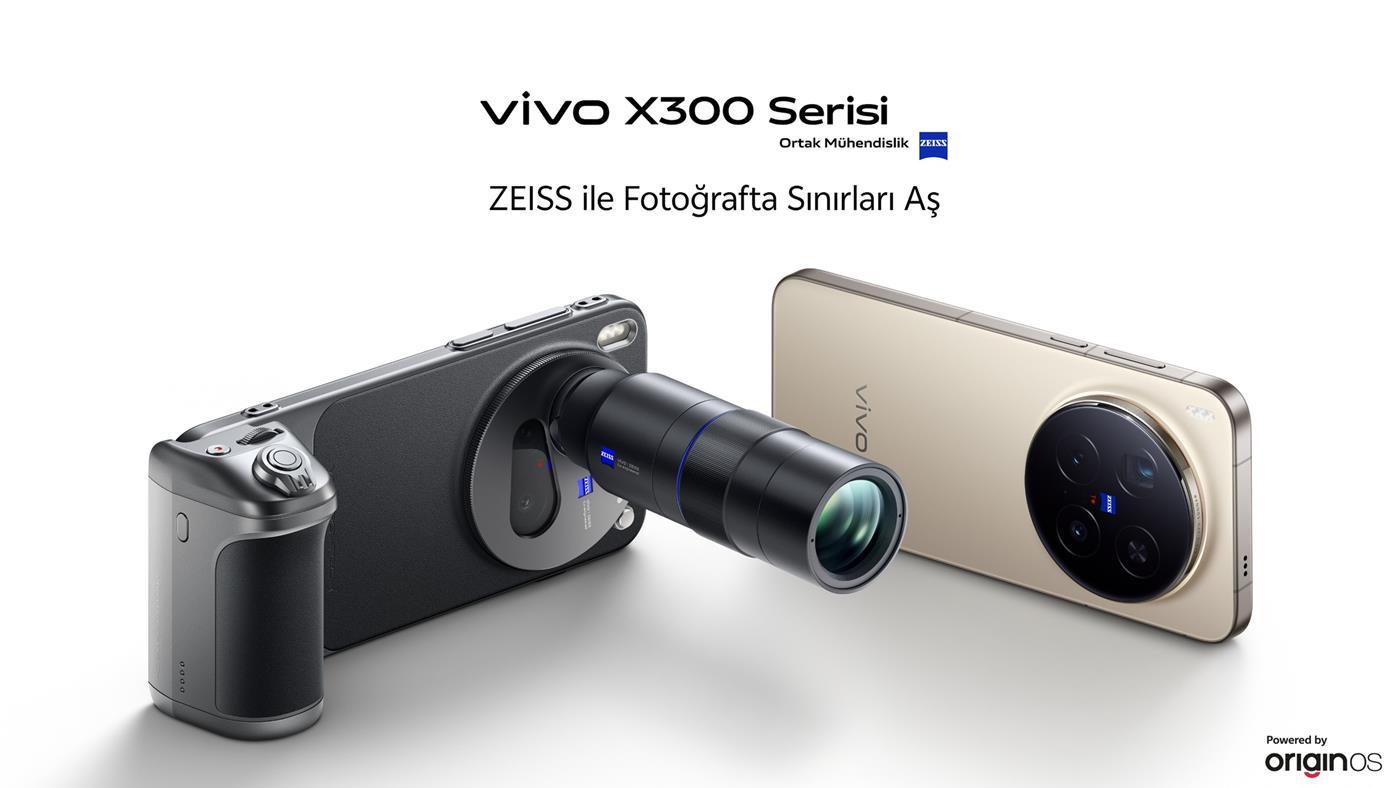
 Küresel pazarlarda piyasaya sürülecek olan Vivo X300 Ultra Geekbench testinde ortaya çıktı. İşte Snapdragon 8 Elite Gen 5, 200 MP kamera sistemi ve Android 16 detaylarıyla lansman öncesi tüm bilgiler:
 Chery ve Jaguar Land Rover iş birliğinde marka olarak hayata dönen Freelander, ilk etapta Çin’de ve ardından küresel pazarda boy gösteren bir SUV markası olacak.
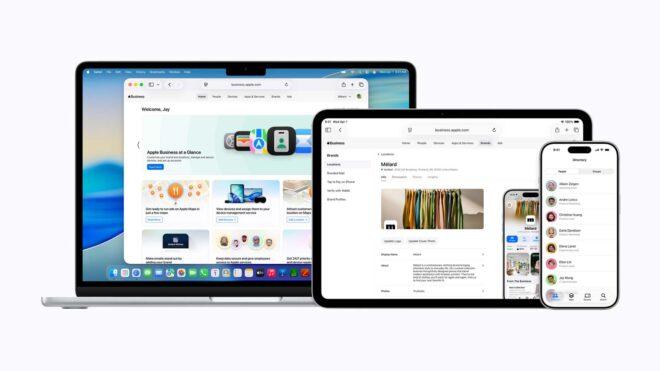
 Apple bugün şirketlerin aygıtlarını zahmetsizce yönetmek, ekip üyelerini gerekli uygulama ve araçlarla donatmak ve uzmanlardan destek almak için ihtiyaç duydukları tüm temel hizmetleri içeren, hepsi bir arada bir platform olan yeni Apple Business’ı duyurdu. Platform hakkında yapılan resmi açıklamada, “Business sayesinde şirketler işlerini verimli ve güvenli şekilde yürütüp büyütebilecek. Apple Business, yerleşik mobil aygıt yönetimi sayesinde işletmelere çalışan gruplarını, aygıt ayarlarını, güvenliği ve uygulamaları kolayca yapılandırma konularında yardımcı olacak ve Blueprint’lerle işe hızlıca koyulmalarını sağlayacak. Buna ek olarak, müşteriler kesintisiz ve gelişmiş iletişim ve iş birliği için artık kendi alan adlarıyla iş mail’i, takvim ve dizin hizmetlerini yapılandırabilecek. Üstelik Apple Business, milyonlarca şirketin Apple Harita, Mail, Cüzdan ve Siri gibi birçok uygulama üzerinden daha geniş kitlelere ulaşmasına ve yerel müşterilerle bağlantı kurmasına da yardımcı olacak. Apple Business, 14 Nisan Salı günü itibarıyla 200’den fazla ülkede ve bölgede kullanıma sunulacak” ifadelerine yer verildi. “Farklı büyüklükteki şirketlerin Apple ürün ve hizmetlerinin gücünden yararlanarak […]
Apple Business platformu tanıtıldı yazısı ilk olarak Teknoloji haberleri – LOG üzerinde yayınlandı.
Every application has secrets: API keys, database credentials, OAuth tokens, encryption keys. How you manage them determines whether those secrets stay secret — and whether your team can actually work with them without emailing each other .env files.
This guide covers the real options in 2025, from basic .env files to production-grade secrets managers.
The Core Problem
Environment variable management has three distinct challenges:
Most teams solve #1 poorly, #2 not at all, and #3 acceptably. This guide covers doing all three well.
The Bad Practice (That Everyone Uses)
The .env file committed to git.
Don’t do this. Secrets in git history are compromised secrets, even if you delete the file later. If your repo is ever public, ever leaked, or ever shared with a contractor — those secrets are exposed forever.
What people do instead (but shouldn’t):
.env files to new team membersAll of these fail in different ways. Here’s how to actually do it.
Option 1: Basic .env With dotenv (Fine for Solo Projects)
The dotenv package loads a .env file into process.env at runtime. It’s simple and universally understood.
Setup:
npm install dotenv
// At the top of your entry file
require('dotenv').config()

// Or with ES modules
import 'dotenv/config'
# .env (NEVER commit this)
DATABASE_URL=postgresql://user:pass@localhost:5432/myapp
API_KEY=sk-abc123
REDIS_URL=redis://localhost:6379

# .env.example (DO commit this)
DATABASE_URL=postgresql://user:pass@localhost:5432/myapp
API_KEY=your-api-key-here
REDIS_URL=redis://localhost:6379
Rules:
.env in .gitignore — always.env.example committed with placeholder values — always.env.example to .env and fill in real valuesLimitations:
Best for: Solo projects, learning, prototypes.
Option 2: dotenvx — Encrypted .env Files
dotenvx is an open-source tool from the creator of the original dotenv. It adds encryption to .env files so you can actually commit them safely.
How it works:
# Install
npm install -g @dotenvx/dotenvx

# Encrypt your .env file
dotenvx encrypt

# .env is now encrypted — safe to commit
# .env.keys contains your private key — DO NOT COMMIT THIS
Your .env file becomes:
#/-------------------[DOTENV_PUBLIC_KEY]--------------------/
#/            public-key encryption for .env files          /
#/       [how it works](https://dotenvx.com/encryption)     /
#/----------------------------------------------------------/
DOTENV_PUBLIC_KEY="025a54c5d04b..."

# .env
DATABASE_URL="encrypted:BGYE53..."
API_KEY="encrypted:BH8f2..."
The encrypted .env can be committed. The .env.keys file (private key) goes in .gitignore and is shared through a separate, secure channel.
Running your app:
# Development (using .env.keys)
dotenvx run -- node server.js

# Production (inject DOTENV_PRIVATE_KEY as env var)
DOTENV_PRIVATE_KEY="your-key" dotenvx run -- node server.js
Why this is good:
Limitations:
Best for: Small teams that want encryption without a full secrets service.
Option 3: Infisical — Open-Source Secrets Manager
Infisical is the most popular open-source secrets management platform. It offers a Vault-like experience with a developer-friendly interface, and you can self-host or use their cloud.
Key features:
CLI usage:
# Install
brew install infisical/get-infisical/infisical

# Login
infisical login

# Initialize project
infisical init

# Run with secrets injected
infisical run -- npm run dev

# Pull secrets to a .env file (for tools that need it)
infisical export --format dotenv > .env
SDK usage (Node.js):
npm install @infisical/sdk
import { InfisicalClient } from "@infisical/sdk"

const client = new InfisicalClient({
  clientId: process.env.INFISICAL_CLIENT_ID,
  clientSecret: process.env.INFISICAL_CLIENT_SECRET,
})

const { secretValue } = await client.getSecret({
  secretName: "DATABASE_URL",
  projectId: "your-project-id",
  environment: "production",
})
Pricing:
Best for: Teams that want open-source but need a full secrets management platform.
Option 4: Doppler — Commercial Secrets Manager with Great DX
Doppler is a commercial secrets management platform focused on developer experience. It’s particularly popular with teams using Vercel, Railway, or similar platforms.
Key features:
CLI usage:
# Install
brew install dopplerhq/cli/doppler

# Login
doppler login

# Configure project
doppler setup

# Run with secrets
doppler run -- npm run dev

# Pull to .env
doppler secrets download --no-file --format env > .env
Vercel integration:
# Sync Doppler secrets to Vercel
doppler secrets download --no-file --format env |
  vercel env add --environment production
Or use the native Vercel ↔ Doppler integration that auto-syncs.
Pricing:
Best for: Small-to-medium teams that want polished tooling and native integration with deployment platforms.
Option 5: AWS Secrets Manager / GCP Secret Manager / Azure Key Vault
For teams already on a cloud provider, using their native secrets service is often the right choice — especially for production workloads.
AWS Secrets Manager:
import { SecretsManagerClient, GetSecretValueCommand } from "@aws-sdk/client-secrets-manager"

const client = new SecretsManagerClient({ region: "us-east-1" })

const response = await client.send(
  new GetSecretValueCommand({ SecretId: "myapp/production/database" })
)

const { DATABASE_URL } = JSON.parse(response.SecretString)
Pros:
Cons:
Best for: Teams with significant AWS workloads that want secrets close to their infrastructure.
Recommended Setup by Team Size
Solo developer / small project
dotenv for local development.env.example committed to repo Small team (2-10 people)
Medium team (10-50 people)
Enterprise / cloud-native
Best Practices Regardless of Tool
Never commit secrets to git. Check your .gitignore includes .env, .env.local, .env.*.local, *.pem, *.key.
Separate by environment. Development secrets should never have production access. Different services, different credentials.
Rotate after exposure. Any secret that was exposed (leaked repo, terminated employee, tool breach) must be rotated immediately — not “eventually.”
Principle of least privilege. Each service should only have access to the secrets it needs. Your API server doesn’t need your database admin credentials.
Audit access. Know who can see which secrets. This matters for both security and compliance.
Don’t log secrets. Audit your logging for accidental secret exposure. Environment variables are particularly easy to accidentally log in error messages.
Quick Comparison
| Tool | Self-hosted | Sync | UI | CI Integration | Cost |
|---|---|---|---|---|---|
| dotenv | Yes | No | No | Manual | Free |
| dotenvx | Yes | Via git | No | Good | Free |
| Infisical | Yes/Cloud | Yes | Yes | Excellent | Free/Paid |
| Doppler | Cloud | Yes | Yes | Excellent | Free tier |
| AWS Secrets Manager | AWS | Yes | AWS Console | Good | ~$0.40/secret/month |
More free tools for developers at DevPlaybook.cc — including JSON Formatter, Base64 Encoder, and 15+ utilities for daily development work.
Level Up Your Dev Workflow
Found this useful? Explore DevPlaybook — cheat sheets, tool comparisons, and hands-on guides for modern developers.
🛒 Get the DevToolkit Starter Kit on Gumroad — 40+ browser-based dev tools, source code + deployment guide included.
Best Free Code Formatters and Linters 2025: The Complete Guide
Code formatting is one of those things teams argue about endlessly until they stop arguing about it entirely — because a formatter has taken the decision off the table. Linting is what catches the bugs that a formatter can’t see. Together, they’re the lowest-effort, highest-ROI investment in code quality a team can make.
This guide covers the best free tools in 2025 across languages, how to configure them, how to integrate them into VS Code and CI, and how to share configs across a team.
Why Formatting and Linting Matter
Formatting is about consistency: tabs vs. spaces, single vs. double quotes, trailing commas, line length. None of these choices matter — what matters is that the whole codebase makes the same choice consistently. When every developer’s editor formats code differently, every pull request has noise from formatting changes mixed in with actual logic changes.
Linting goes further: it catches potential bugs, enforces best practices, and flags patterns that are technically valid but commonly lead to mistakes. A linter won’t catch every bug, but it catches the ones that are always wrong — and it does it in milliseconds.
The compounding benefits:
The question isn’t whether to use formatters and linters. The question is which ones.
Prettier: The Opinionated Formatter
Prettier is the dominant code formatter for JavaScript, TypeScript, CSS, HTML, JSON, Markdown, and more. Its defining characteristic is that it’s opinionated — it has minimal configuration, and it overrides your choices with its own. This is a feature, not a bug. The whole point is to end formatting debates by removing the decision entirely.
Installation
npm install --save-dev prettier
Basic Config
Create .prettierrc in your project root:
{
  "semi": true,
  "singleQuote": true,
  "tabWidth": 2,
  "trailingComma": "es5",
  "printWidth": 100,
  "arrowParens": "avoid"
}
Create .prettierignore:
node_modules
dist
build
coverage
*.min.js
Running Prettier
# Check files without modifying (useful for CI)
npx prettier --check .

# Format all files in place
npx prettier --write .

# Format a specific file
npx prettier --write src/app.js
VS Code Integration
Install the Prettier – Code formatter extension (esbenp.prettier-vscode). Then add to your VS Code settings (settings.json):
{
  "editor.defaultFormatter": "esbenp.prettier-vscode",
  "editor.formatOnSave": true,
  "[javascript]": {
    "editor.defaultFormatter": "esbenp.prettier-vscode"
  },
  "[typescript]": {
    "editor.defaultFormatter": "esbenp.prettier-vscode"
  }
}
With formatOnSave: true, every file is formatted the moment you hit save. No manual formatting steps.
ESLint: Catching Bugs Before Runtime
ESLint is the linting standard for JavaScript and TypeScript. Unlike Prettier, it’s not opinionated — it’s highly configurable. You choose which rules to enable, what severity level to apply, and which plugins to use.
Installation and Setup
npm install --save-dev eslint
npx eslint --init
The --init wizard walks you through setup and creates your config. For TypeScript support:
npm install --save-dev @typescript-eslint/parser @typescript-eslint/eslint-plugin
Modern Flat Config (ESLint v9+)
ESLint v9 introduced a new “flat config” format using eslint.config.js (replacing .eslintrc). The new format is cleaner and more explicit:
// eslint.config.js
import js from '@eslint/js';
import tseslint from 'typescript-eslint';

export default [
  js.configs.recommended,
  ...tseslint.configs.recommended,
  {
    rules: {
      'no-unused-vars': 'warn',
      'no-console': 'warn',
      'prefer-const': 'error',
      'no-var': 'error',
      '@typescript-eslint/no-explicit-any': 'warn',
    }
  }
];
Severity Levels
"error" — fails the lint check, blocks CI"warn" — shows a warning but doesn’t fail"off" — disables the rule Key Plugins Worth Installing
| Plugin | Purpose |
|---|---|
eslint-plugin-react |
React-specific rules |
eslint-plugin-react-hooks |
Rules of Hooks enforcement |
eslint-plugin-jsx-a11y |
Accessibility rules for JSX |
eslint-plugin-import |
Import/export validation |
eslint-plugin-security |
Catches common security patterns |
eslint-plugin-unicorn |
Enforces modern JavaScript best practices |
Integrating ESLint with Prettier
ESLint and Prettier can conflict — both may have opinions about the same code. The solution is eslint-config-prettier, which disables all ESLint rules that might conflict with Prettier:
npm install --save-dev eslint-config-prettier
Add "prettier" as the last item in your extends array:
// eslint.config.js
import prettier from 'eslint-config-prettier';

export default [
  js.configs.recommended,
  ...tseslint.configs.recommended,
  prettier,  // Must be last — disables conflicting rules
  {
    rules: {
      // Your custom rules here (non-formatting only)
    }
  }
];
Rule of thumb: Prettier handles formatting, ESLint handles code quality. Don’t overlap.
Biome: The All-in-One Newcomer
Biome is the new challenger that combines formatting and linting into a single tool. It’s written in Rust, which makes it dramatically faster than both Prettier and ESLint. For large codebases, this matters.
Why Biome Is Worth Watching
biome.json replaces .prettierrc + .eslintrc
Installation
npm install --save-dev --save-exact @biomejs/biome
npx biome init
Configuration (biome.json)
{
  "$schema": "https://biomejs.dev/schemas/1.6.0/schema.json",
  "organizeImports": {
    "enabled": true
  },
  "linter": {
    "enabled": true,
    "rules": {
      "recommended": true,
      "suspicious": {
        "noExplicitAny": "warn"
      }
    }
  },
  "formatter": {
    "enabled": true,
    "indentStyle": "space",
    "indentWidth": 2,
    "lineWidth": 100
  },
  "javascript": {
    "formatter": {
      "quoteStyle": "single",
      "trailingCommas": "es5",
      "semicolons": "always"
    }
  }
}
Running Biome
npx biome check .          # Lint + format check (no writes)
npx biome check --apply .  # Lint + format and apply safe fixes
npx biome format --write . # Format only, apply writes
When to use Biome vs. Prettier + ESLint:
Biome doesn’t yet have the full plugin ecosystem of ESLint, but it covers the most important rules out of the box.
Language-Specific Tools
Python: Black + Ruff
Black is Python’s answer to Prettier — opinionated, fast, and uncompromising. It formats your Python code with almost no configuration.
pip install black
black .                    # Format all Python files
black --check .            # Check without modifying (CI)
black --diff .             # Show what would change
Black’s only meaningful config option is line length (default 88):
# pyproject.toml
[tool.black]
line-length = 88
target-version = ['py311']
Ruff is the linter equivalent — extremely fast (written in Rust), replaces Flake8, isort, and many other Python tools:
pip install ruff
ruff check .
ruff check --fix .
# pyproject.toml
[tool.ruff]
line-length = 88
select = ["E", "F", "I", "N", "UP"]
ignore = ["E501"]
Go: gofmt and golangci-lint
Go ships with gofmt built in — no installation required, no configuration. Run it and your code is formatted to the Go standard. There is no debate about Go formatting.
gofmt -w .                 # Format all .go files in place
gofmt -d .                 # Show diff without modifying
For linting, golangci-lint aggregates many Go linters into one fast runner:
go install github.com/golangci/golangci-lint/cmd/golangci-lint@latest
golangci-lint run
Rust: rustfmt and Clippy
Rust ships with both formatters and linters as part of the official toolchain:
rustup component add rustfmt clippy

cargo fmt              # Format all Rust code
cargo fmt --check      # Check only (CI)
cargo clippy           # Run the Clippy linter
cargo clippy -- -D warnings   # Treat warnings as errors (strict CI)
rustfmt is configured via rustfmt.toml:
max_width = 100
edition = "2021"
imports_granularity = "Module"
CI Integration
Pre-Commit Hooks
pre-commit runs checks before every git commit. If a check fails, the commit is blocked.
pip install pre-commit
Create .pre-commit-config.yaml:
repos:
  - repo: https://github.com/pre-commit/pre-commit-hooks
    rev: v4.5.0
    hooks:
      - id: trailing-whitespace
      - id: end-of-file-fixer
      - id: check-merge-conflict

  - repo: https://github.com/psf/black
    rev: 24.3.0
    hooks:
      - id: black

  - repo: https://github.com/astral-sh/ruff-pre-commit
    rev: v0.3.0
    hooks:
      - id: ruff
        args: [--fix]

  - repo: https://github.com/biomejs/pre-commit
    rev: v0.1.0
    hooks:
      - id: biome-check
        additional_dependencies: ["@biomejs/[email protected]"]
pre-commit install          # Install hooks (run once per repo)
pre-commit run --all-files  # Run manually on all files
GitHub Actions
# .github/workflows/lint.yml
name: Lint and Format Check

on: [push, pull_request]

jobs:
  lint:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4

      - name: Set up Node.js
        uses: actions/setup-node@v4
        with:
          node-version: '20'
          cache: 'npm'

      - name: Install dependencies
        run: npm ci

      - name: Check formatting (Prettier)
        run: npx prettier --check .

      - name: Lint (ESLint)
        run: npx eslint . --max-warnings 0

  lint-python:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4
      - uses: actions/setup-python@v5
        with:
          python-version: '3.11'

      - name: Install tools
        run: pip install black ruff

      - name: Check formatting (Black)
        run: black --check .

      - name: Lint (Ruff)
        run: ruff check .
Online Formatters
Sometimes you just need to quickly format a snippet without setting up a local tool. DevPlaybook provides free browser-based formatters at devplaybook.cc:
These tools are useful for one-off formatting tasks, validating API responses, or quickly cleaning up a snippet before pasting it into documentation.
Team Setup Guide: Sharing Configs
The Problem
Individual developers can have formatters installed, but if everyone’s config differs, the formatting still varies. The solution: commit your config files to the repository so everyone uses the same settings.
Files to Commit
.prettierrc             # Prettier config
.prettierignore         # Prettier exclusions
eslint.config.js        # ESLint config
biome.json              # Biome config (if using Biome)
.editorconfig           # Universal editor settings
.pre-commit-config.yaml # Pre-commit hooks
.editorconfig
.editorconfig is supported by almost every editor natively and defines basic formatting rules across all languages:
root = true

[*]
charset = utf-8
end_of_line = lf
insert_final_newline = true
trim_trailing_whitespace = true
indent_style = space
indent_size = 2

[*.py]
indent_size = 4

[Makefile]
indent_style = tab
VS Code Workspace Settings
Add a .vscode/settings.json file to the repository:
{
  "editor.formatOnSave": true,
  "editor.codeActionsOnSave": {
    "source.fixAll.eslint": "explicit"
  },
  "editor.defaultFormatter": "esbenp.prettier-vscode",
  "eslint.validate": ["javascript", "typescript", "jsx", "tsx"]
}
And recommend extensions via .vscode/extensions.json:
{
  "recommendations": [
    "esbenp.prettier-vscode",
    "dbaeumer.vscode-eslint",
    "biomejs.biome"
  ]
}
When a developer opens the project, VS Code prompts them to install the recommended extensions. Combined with committed config files, this means any developer who clones the repo is fully set up in minutes.
npm Scripts
Add standard lint/format scripts to package.json:
{
  "scripts": {
    "lint": "eslint . --max-warnings 0",
    "lint:fix": "eslint . --fix",
    "format": "prettier --write .",
    "format:check": "prettier --check .",
    "check": "npm run format:check && npm run lint"
  }
}
The check script runs both format and lint checks — useful in CI pipelines.
Choosing Your Stack in 2025
| Scenario | Recommended Stack |
|---|---|
| New JS/TS project | Biome (all-in-one, fast) |
| Existing JS/TS project | Prettier + ESLint |
| Python project | Black + Ruff |
| Go project | gofmt + golangci-lint |
| Rust project | rustfmt + Clippy |
| Multi-language monorepo | pre-commit with per-language tools |
The most important thing isn’t which tool you pick — it’s that you automate it. A formatter you have to run manually is a formatter you’ll forget to run. Hook it into your editor save action and your CI pipeline, and code quality becomes a property of the system, not a personal discipline.
Level Up Your Dev Workflow
Found this useful? Explore DevPlaybook — cheat sheets, tool comparisons, and hands-on guides for modern developers.
🛒 Get the DevToolkit Starter Kit on Gumroad — 40+ browser-based dev tools, source code + deployment guide included.

Hey everyone! Honestly, it feels so good to be sitting down and writing to you all again. I want to start with a massive apology for the radio silence and the long gap between my last few posts. Life has a funny way of getting busy, but I’ve missed this community and our deep dives into the future of tech.
We’re talking about a problem that has been bugging me all through 2025 and into 2026: AI situational awareness. Let’s dive in.
The “Goldfish” Problem: Why Your AI is Gaslighting Your Users 🐠🌀
Look, we need to have a genuine heart-to-heart about your AI agents. We’re well into 2026, and yet, most AI “agents” still have the situational awareness of a goldfish in a blender. It’s a bit heartbreaking, isn’t it?
You know the feeling: You’ve spent weeks perfecting your system prompts, the UI is looking like a work of art, and your LLM is sharp. But the second a user actually does something—like upgrading a subscription, changing a delivery address, or updating their profile—the AI is the absolute last one to know. It’s like the “memory” of your agent is stuck in a permanent time lag, trapped in a 2024 batch-processing nightmare.
Imagine you’re building the ultimate AI concierge for a luxury travel app.
Sarah is now officially being gaslit by an algorithm. 🤦♂️ The immersion? Totally gone. The trust? Shattered. This happens because the “Transactional Brain” (Aurora) isn’t talking to the “Analytical Memory” (Redshift) fast enough. We need a way to move that data so quickly it feels like magic. Today, we are fixing that with Live Memory using Amazon Aurora Zero-ETL and Redshift Vector Search.
Step 1: The “Wormhole” (Zero-ETL) 🚀
In the “old days” (way back in 2024), moving data from Aurora to Redshift meant building a “Glue” pipeline. It was like trying to build a bridge between two islands using nothing but popsicle sticks, duct tape, and a whole lot of hope. It broke constantly, it cost a fortune, and it was painfully slow.
Zero-ETL is the modern way to handle this. Think of it as a native “wormhole” between Aurora and Redshift. When you enable it, AWS handles all the heavy lifting and plumbing behind the scenes. No Python scripts to debug, no Lambda triggers to monitor, and absolutely zero drama.

Why this is the “Secret Sauce” for your Agent:
Step 2: From “Rows” to “Recall” (Vector Search) 🧠
Okay, so the data has successfully teleported into Redshift. But here’s the catch: Redshift is a warehouse full of structured tables, and AI Agents don’t really “think” in tables—they think in Vectors (mathematical representations of meaning).
In the past, you’d have to ship this data again to a dedicated vector database. But that just adds more lag! Instead, we use Redshift’s Native Vector Search. This keeps your “Live Memory” in one single, high-performance place. To make this work, we set up a Materialized View in Redshift that automatically calls Amazon Bedrock to turn those new rows into vectors on the fly.
-- The "I don't have a goldfish memory anymore" Query
CREATE MATERIALIZED VIEW live_user_context AS
SELECT
    user_id,
    event_description,
    -- This calls Bedrock to create a vector on the fly!
    amazon_bedrock_embed(event_description) as semantic_vector
FROM aurora_synced_data.user_logs;
Step 3: The “Aha!” Moment 🔍
Now, let’s replay the Sarah scenario. When she asks about her flight, the AI Agent sends a vector query to Redshift. Redshift looks at the most recent events—including the one that landed just 10 seconds ago—and finds the “Canceled Paris / Booked Rome” entry.
The Agent responds: “I see you switched to the Rome trip—great choice! That flight leaves at 8 PM. Should I book a car to the airport?”
Boom. You just saved the user experience. 🥳 You’ve moved from a “chatbot” to a genuine “agent” that understands the present moment.
By The Numbers: Is it worth your time? 📈
We ran some benchmarks to see just how much of a difference this “Live Memory” architecture actually makes. When you compare the old “Batch” world to the new “Zero-ETL” world, the latency gap is massive.

Developer Happiness:
Pro-Tips for the Modern ML Engineer 🛠️
WHERE user_id = '123') to make your search lightning fast. Final Thoughts
Anyway, it feels amazing to be back in the flow and sharing these breakthroughs with you all again. The leap from “static” AI to “live” agents is one of the most exciting shifts we’re seeing this year, and I can’t wait to see how you all implement these “wormholes” in your own stacks. If you run into any snags or just want to geek out over vector search optimizations, drop a comment below or find me over on Dev.to! I promise the next article won’t take nearly as long to reach your screens. Until next time — stay curious, keep building, and let’s make those agents a whole lot smarter. 🚀✨
Best Cron Job Generators and Testers (Free, 2026) — Compared
Cron is 50 years old and still running production workloads at companies of every size. Daily database backups, weekly report emails, hourly cache invalidations, nightly ML training jobs — cron (or a cron-like scheduler) handles an enormous fraction of the world’s scheduled computing.
The syntax is terse enough that even experienced developers reach for a cron expression generator when they need something beyond “run every hour.” The */5 * * * * pattern is memorable. The “every weekday at 9am EST only during business days” pattern is not.
We tested 7 free cron tools — generators, validators, and testers — to find which ones are actually useful for production work.
Understanding Cron Syntax First
A cron expression has 5 (or 6, in extended formats) fields:
* * * * *
│ │ │ │ │
│ │ │ │ └─── Day of week (0-7, where 0 and 7 = Sunday)
│ │ │ └───── Month (1-12)
│ │ └─────── Day of month (1-31)
│ └───────── Hour (0-23)
└─────────── Minute (0-59)
Some schedulers (like Quartz, AWS EventBridge, and Spring) use a 6-field format that adds a seconds field at the start:
* * * * * *
│ │ │ │ │ │
│ │ │ │ │ └─── Day of week
│ │ │ │ └───── Month
│ │ │ └─────── Day of month
│ │ └───────── Hour
│ └─────────── Minute
└─────────── Second (0-59)
Know which format your scheduler expects before you write or paste a cron expression. Mixing them up is the #1 source of cron misconfiguration.
Special syntax:
* — every value*/n — every n values (e.g., */15 = every 15 minutes)n-m — range (e.g., 9-17 = hours 9 through 17)n,m — list (e.g., 1,3,5 = Monday, Wednesday, Friday)@hourly, @daily, @weekly, @monthly, @yearly — shorthand aliases The 7 Tools We Tested
1. DevPlaybook Cron Generator
URL: devplaybook.cc/tools/cron-generator
DevPlaybook’s Cron Generator is built for the workflow where you know what you want to schedule in plain English and need the cron expression.
What it does well:
The plain-English input approach is effective. Describe your schedule (“every weekday at 9:30am”), get the cron expression. This is faster than remembering field order for simple schedules, and it avoids the common mistake of putting the minute and hour fields in the wrong order.
The “next run times” preview shows the next 5 scheduled executions with actual timestamps (including your local timezone). This catches the most common production bug: scheduling something for “every hour” and only realizing after deployment that it’s running at :00 of every hour GMT, not your local timezone.
The generated expression is accompanied by a plain-English description (“At 9:30 AM, Monday through Friday”) so you can double-check that the expression matches your intent before copying it.
What could be better:
Doesn’t support 6-field (Quartz/Spring/AWS) expressions yet.
No syntax for “last day of the month” or other extended cron features used by some schedulers.
Best for: Developers who know the schedule they want but aren’t fluent in cron syntax. The next-run preview is the most valuable feature for avoiding timezone mistakes.
2. DevPlaybook Cron Validator
URL: devplaybook.cc/tools/cron-validator
The Cron Validator does the opposite of the Generator: you paste an existing cron expression and it tells you whether it’s valid and what it means.
What it does well:
Immediately tells you if an expression is valid and why it’s invalid if not. Error messages are specific: “day of week value 8 is out of range (0-7)” is more useful than “invalid expression.”
The description output is clear: 0 2 * * 1 becomes “At 02:00 AM, only on Monday.” This is invaluable for reviewing cron jobs in code review or documentation.
Shows the next 10 scheduled run times. Ten is the right number — it’s enough to confirm the pattern (not just the first occurrence) without being overwhelming.
Best for: Reviewing cron expressions in existing code, validating before deployment, code review.
3. DevPlaybook Cron Builder
URL: devplaybook.cc/tools/cron-builder
The Cron Builder is a visual interface for constructing cron expressions field by field.
What it does well:
Dropdown menus for each field with valid value ranges. You can’t enter an invalid value because the inputs constrain the options. This is useful for developers new to cron syntax who want to learn by building.
The live preview updates as you adjust each field, showing both the expression and a description. Watching how the expression changes as you select “every Tuesday” vs “every Tuesday and Thursday” teaches the syntax faster than reading documentation.
Supports multiple selection for lists (comma-separated) and range selection, which the UI makes significantly more discoverable than raw syntax.
Best for: Learning cron syntax, building expressions with complex field combinations (multiple days, multiple hours).
4. Crontab.guru
URL: crontab.guru
Crontab.guru is the most widely used cron expression explainer. When developers search for “cron expression checker,” this is typically what they find and use.
What it does well:
The “random” feature teaches cron syntax by showing you valid expressions and explaining them. Spend 5 minutes clicking Random and you’ll have a working understanding of the syntax.
The explanation is clean and in a single line: * * * * * → “At every minute.” Clear, unambiguous.
The interface is deliberately minimal — just an input field and the explanation. This is intentional and works well for quick checks.
URL state: the expression is in the URL, so you can bookmark or share a specific expression.
What could be better:
No “next run times” preview. You can see what the expression means but not when it will actually fire.
No validation of the expression against a specific timezone.
No 6-field support.
Best for: Quick expression checking, learning cron syntax, sharing expressions via URL.
5. CronMaker
URL: cronmaker.com
CronMaker supports both 5-field and 6-field (Quartz) cron expressions, which makes it uniquely useful for Java Spring and AWS developers.
What it does well:
The Quartz scheduler support is the reason to use CronMaker. Spring Boot jobs, Quartz schedulers, and AWS EventBridge (CloudWatch Events) use different syntax than standard Unix cron. CronMaker handles all of these.
The expression builder supports Quartz-specific features: L for “last” (last day of month, last Friday of month), W for “nearest weekday,” and # for “nth day of week” (e.g., 2#3 = second Tuesday of the month).
The next-run preview includes 10 scheduled times.
What could be better:
The UI is dated. The layout is functional but clearly hasn’t been updated in years. For a utility tool this might not matter, but it does affect readability.
Best for: Spring Boot, Quartz Scheduler, AWS EventBridge — any context where you need 6-field cron or Quartz-specific syntax.
6. FreeFormatter Cron Validator
URL: freeformatter.com/cron-expression-generator-quartz.html
FreeFormatter’s cron tool focuses on Quartz cron validation.
What it does well:
Handles Quartz syntax. Has a visual field builder for the 6-field format.
What could be better:
Limited additional features. Doesn’t explain what the expression means in plain English. Useful as a validation tool, not a learning tool.
Best for: Quick Quartz expression validation.
7. Cron Expression Descriptor
URL: cronexpressiondescriptor.azurewebsites.net
A tool focused entirely on converting cron expressions to plain English.
What it does well:
Handles complex expressions well, including multi-value fields and ranges. The plain-English output is accurate.
What could be better:
The URL and UX are rough. It’s a port of the open-source CronExpressionDescriptor library.
Best for: Getting a plain-English description of a complex expression when other tools fall short.
Tool Comparison
| Tool | Generator | Validator | Visual Builder | Next Runs | Quartz | Timezone |
|---|---|---|---|---|---|---|
| DevPlaybook Cron Gen | ✅ | ✅ | ❌ | ✅ | ❌ | ✅ |
| DevPlaybook Cron Validator | ❌ | ✅ | ❌ | ✅ | ❌ | ❌ |
| DevPlaybook Cron Builder | ✅ | ✅ | ✅ | ✅ | ❌ | ❌ |
| Crontab.guru | ✅ | ✅ | ❌ | ❌ | ❌ | ❌ |
| CronMaker | ✅ | ✅ | ✅ | ✅ | ✅ | ❌ |
| FreeFormatter | ✅ | ✅ | ✅ | ✅ | ✅ | ❌ |
| Cron Descriptor | ❌ | ✅ | ❌ | ❌ | ❌ | ❌ |
Common Cron Expressions Reference
Every minute
* * * * *
Every 5 minutes
*/5 * * * *
Every hour (at minute :00)
0 * * * *
Every day at midnight
0 0 * * *
Every day at 6am
0 6 * * *
Every weekday at 9am
0 9 * * 1-5
Every Monday at noon
0 12 * * 1
Every first day of the month at midnight
0 0 1 * *
Every 15 minutes, business hours only (9am-5pm, Mon-Fri)
*/15 9-17 * * 1-5
Every Sunday at 3am (good for weekly maintenance)
0 3 * * 0
Quarterly (first day of Jan, Apr, Jul, Oct)
0 0 1 1,4,7,10 *
Every 6 hours
0 */6 * * *
The Timezone Trap (and How to Avoid It)
The #1 production mistake with cron jobs is timezone confusion. Most cron daemons on Linux servers run in UTC. If you schedule 0 9 * * * thinking it runs at 9am local time, it will actually run at 9am UTC — potentially 5-8 hours off depending on your timezone and daylight saving time.
Always verify:
DevPlaybook’s Cron Generator shows next run times in both UTC and your local timezone for this reason.
On Linux, check the system timezone:
timedatectl
# or
cat /etc/timezone
Override cron’s timezone per-user:
# In your crontab (crontab -e)
CRON_TZ=America/New_York
0 9 * * * /path/to/job
For modern cloud infrastructure (AWS Lambda, Google Cloud Run, etc.), the scheduler runs in UTC by default. Always write your expressions in UTC and convert to local time for documentation.
Cron Alternatives Worth Knowing
Traditional cron has limitations: no retry logic, no dependencies between jobs, no distributed execution, limited observability.
For production job scheduling beyond simple periodic tasks:
Airflow — The industry standard for DAG-based workflow scheduling. Overkill for simple jobs, essential for data pipelines with dependencies.
Temporal — Durable execution platform with retry logic, timeouts, and visibility. Good for long-running workflows.
pg_cron — Cron scheduler for PostgreSQL. If your jobs are mostly database operations, running them inside the database reduces network hops and simplifies monitoring.
GitHub Actions with schedule trigger — Good for CI/CD-adjacent jobs: report generation, nightly builds, automated releases.
# GitHub Actions example
on:
  schedule:
    - cron: '0 2 * * *'  # Every day at 2am UTC
Heroku Scheduler — If you’re on Heroku, the scheduler add-on handles cron-like jobs with a simple UI.
For most teams, standard cron (with a tool like Kubernetes CronJobs for containerized workloads) handles 80% of scheduling needs. Save the orchestration platform for when you actually need retry logic, inter-job dependencies, or observability.
Debugging Cron Jobs That Don’t Run
When a cron job doesn’t fire, the debugging order is:
1. Check the crontab is installed
crontab -l          # list current user's crontab
sudo crontab -l     # list root's crontab
2. Check if cron is running
systemctl status cron    # Debian/Ubuntu
systemctl status crond   # RHEL/CentOS
3. Check cron logs
grep CRON /var/log/syslog            # Ubuntu/Debian
grep CRON /var/log/cron              # RHEL/CentOS
journalctl -u cron --since "1 hour ago"
4. Validate the expression
Paste it into DevPlaybook Cron Validator and confirm it’s valid and scheduled when you expect.
5. Check the script runs manually
/bin/bash -c "/path/to/your/script.sh"
Cron runs with a minimal environment. If the script works manually but not in cron, the issue is usually a missing PATH, missing environment variables, or a relative path.
6. Check file permissions
ls -la /path/to/your/script.sh
The script must be executable by the user the cron job runs as.
Our Recommendations
Quickest cron expression lookup: Crontab.guru — fast, reliable, zero friction.
Best for building new expressions: DevPlaybook Cron Generator — plain-English input with timezone-aware next-run preview.
Best for validating existing expressions: DevPlaybook Cron Validator — 10 next-run times with clear error messages.
Best for learning cron syntax: DevPlaybook Cron Builder — visual field-by-field construction teaches the syntax as you use it.
Best for Spring/Quartz/AWS: CronMaker — the only free tool with proper Quartz expression support.
For most developers, the workflow is: use DevPlaybook Cron Generator to build the expression, use DevPlaybook Cron Validator to verify it before deploying, and use Crontab.guru for quick “what does this mean” lookups when reviewing code.
Level Up Your Dev Workflow
Found this useful? Explore DevPlaybook — cheat sheets, tool comparisons, and hands-on guides for modern developers.
🛒 Get the DevToolkit Starter Kit on Gumroad — 40+ browser-based dev tools, source code + deployment guide included.