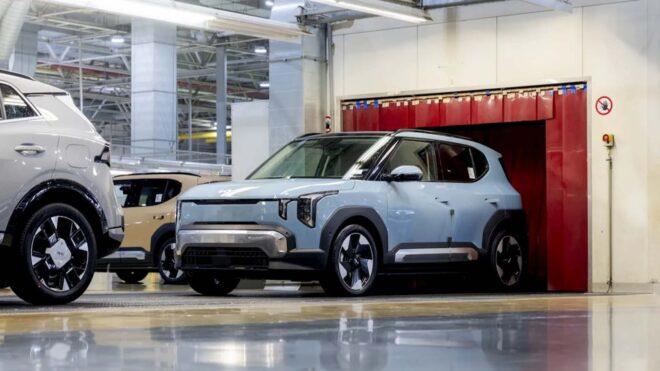
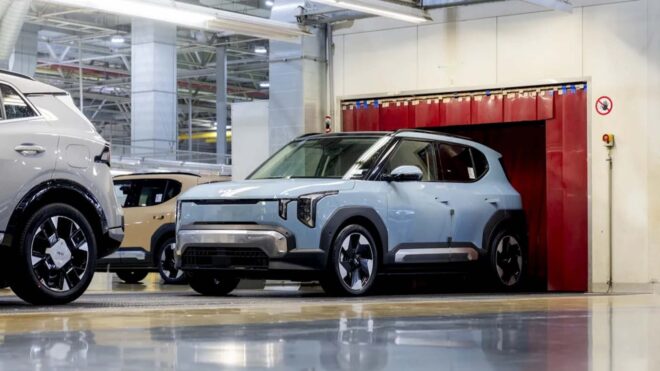
Türkiye’de de satılacak Kia EV2, üretim bandından inmeye başladı

Kia EV2

Kia EV2Tamamen elektrikli kompakt otomobil modeli Kia EV2, önümüzdeki ay başlayacak teslimatlar öncesinde şirketin Slovakya’da yer alan fabrikasındaki üretim bandından inmeye başladı. Kia Türkiye Genel Müdürü Can Ağyel, Emre Özpeynirci’nin CNBC-e’deki Oto Ekonomi programında EV2’nin Türkiye satış fiyatı ve tarihi hakkında açıklamalarda bulunmuştu. Merak edilen aracı Türkiye’ye 1 milyon 800 bin TL bandında getirmek istediklerini ve bunun için genel merkezle görüşmeler gerçekleştirdiklerini belirten Ağyel, yüksek sayıda getirmek istedikleri kompakt elektriklinin mayıs sonu ya da haziran ayında Türkiye’de satılmaya başlanacağını söyledi. EV2’nin Türkiye’de uzaktan bağlantılı olarak sunulacak ilk modelleri olacağını da aktaran Ağyel, yeni model yılına sahip diğer elektrikli araçlarda da bağlantılı hizmetlerin bulunacağını ifade etti. EV2 için 42,2 kWh ve 61,0 kWh olmak üzere iki farklı batarya paketi sunuluyor. 42,2 kWh bataryalı versiyon 317 km menzil vadediyor ve 145 beygir gücünde bir elektrik motoru taşıyor. 61,0 kWh bataryalı versiyon ise 448 km menzile sahip. 400 volt mimarili model, 22 kW AC […]

Türkiye’de de satılacak Kia EV2, üretim bandından inmeye başladı yazısı ilk olarak Teknoloji haberleri – LOG üzerinde yayınlandı.

X, X Pro’yu bir anda Premium+ özelliği yaptı

X LOG Tasarım

X LOG TasarımBugün çok tepki çeken bir adım atan X, Twitter döneminde “TweetDeck” olarak isimlendirilen X Pro’yu herhangi bir ön duyuru yapmadan Premium+ özelliği haline getirdi. Bu konuda yaptığı açıklamada, “26 Mar 2026 itibarıyla Pro’ya yalnızca Premium+ ve üzeri planlarda erişilebilir. Sistemi kullanmak için lütfen planını yükselt.” diyen şirket, X Pro’nun şimdiye kadar aylık 150 TL fiyatı bulunan standart “Premium” aboneliği ile kullanılmasına izin veriyordu. Premium+ için aylık 1.691 TL talep eden şirket, bu beklenmedik hamlesiyle sırf altyapının sağladığı gerçek zamanlı akış ve aynı anda birden fazla akışın takip edilmesine imkan tanıyan yapı için Premium aboneliği alan çok sayıda kullanıcıyı kaybedebilir.

X, X Pro’yu bir anda Premium+ özelliği yaptı yazısı ilk olarak Teknoloji haberleri – LOG üzerinde yayınlandı.

CI/CD: Accelerating Software Delivery Through Automation

In the fast-paced world of software development, businesses need to deliver features quickly, reliably, and at scale. This is where CI/CD (Continuous Integration and Continuous Deployment/Delivery) comes into play. CI/CD is a set of modern practices that automate the process of building, testing, and deploying applications, enabling teams to release software faster while maintaining high quality.

What Is CI/CD?
Continuous Integration (CI)
CI is the practice of frequently merging code changes from multiple developers into a shared repository. Each merge triggers automated builds and tests, helping detect errors early, reduce integration problems, and ensure code quality.
Continuous Deployment/Delivery (CD)
CD automates the process of deploying code to production.
Continuous Delivery: Code is automatically prepared for release but requires manual approval for production deployment.
Continuous Deployment: Every change that passes automated tests is deployed directly to production.

Together, CI/CD ensures faster, reliable, and repeatable software delivery cycles.

Key Components of CI/CD
Source Code Repository – Centralized code management (e.g., GitHub, GitLab).
Build Automation – Compiles and packages code automatically.
Automated Testing – Unit, integration, and end-to-end tests ensure code quality.
Deployment Automation – Scripts and pipelines push code to staging and production environments.
Monitoring & Feedback – Detects issues post-deployment and enables rapid remediation.
Benefits of CI/CD
Faster Time-to-Market: Automates repetitive tasks and reduces manual errors.
Higher Code Quality: Continuous testing catches bugs early, ensuring stable releases.
Improved Collaboration: Developers can merge changes frequently without conflicts.
Reduced Risk: Smaller, incremental updates reduce the impact of errors.
Operational Efficiency: Automated pipelines save time and effort across teams.
Popular CI/CD Tools
Jenkins – Open-source automation server for building and deploying pipelines.
GitLab CI/CD – Integrated CI/CD pipelines in GitLab repositories.
CircleCI – Cloud-based CI/CD for fast and scalable automation.
Travis CI – Continuous integration platform for automated builds and tests.
AWS CodePipeline / Azure DevOps / Google Cloud Build – Cloud-native CI/CD solutions.
CI/CD Best Practices
Automate Everything: Build, test, and deploy without manual intervention.
Use Version Control Effectively: Maintain a single source of truth for code.
Implement Comprehensive Testing: Include unit, integration, and security tests.
Monitor Deployments: Continuously track application performance and errors.
Adopt Incremental Releases: Smaller changes are easier to test and deploy.
CI/CD and Cloud Integration

CI/CD pipelines integrate seamlessly with cloud services, enabling scalable, flexible, and cost-efficient software delivery. Platforms like AWS, Azure, and Google Cloud, along with automation tools like Jenkins, allow developers to deploy globally, manage resources efficiently, and ensure high availability.

Conclusion

CI/CD is the backbone of modern DevOps, helping organizations deliver high-quality software faster, reduce risk, and improve collaboration. By automating integration, testing, and deployment processes, CI/CD empowers teams to focus on innovation and customer value, ensuring software is reliable, scalable, and continuously improving.

The point of planning

In software development, we love to make plans. We plan everything from 2-week sprints to 5 or more year roadmaps. And yet I sometimes think that the point of planning is misunderstood.

The point of having a plan, for me, is not to have a concrete set of steps. Well, it is that, but that’s not the real value of it. The point is understanding the why of the plan, and the how of the steps.

The why of the plan is this: Why does this plan make sense? Why does this plan bring us closer to fulfilling our goals? Without a purpose behind it, a plan is meaningless. I would even go so far as to say that sometimes having a fixed plan at all is counterproductive. Sometimes the product may be in an exploratory phase, and the only plan would be to try a lot of things and see what works. But the why behind this plan is clear: To evaluate a lot of options. Then we could go into the details and schedule the evaluations and timelines for the options we want to explore. The point is that the goal dictates the plan. Not the other way around.

And on a smaller scale we have to understand how the steps of the plan contribute to achieving the goal of the plan, how they contribute to fulfilling the why. The point of this understanding is that often plans can’t be executed exactly as they were initially created. But if we understand how something we can no longer do was supposed to contribute to the end goal, then we can intelligently search for a replacement to that something. We can do this because we understand the new situation we’re in and we know that we need to find something else to do that fulfills the purpose of the step we wanted to take, but can’t.

Actually, I would summarize this whole article with one concrete advice: For every component of a plan, understand the purpose of the component. For the plan as a whole that is the why, and for the steps of the plan that is the how.

Thanks for reading 🙂

A Zero-Rake Coin Flip on Base vs Crypto Casinos

Why a Single Coin Flip Can Be Fairer Than an Entire Crypto Casino

Most “crypto casinos” take the Web2 playbook, bolt a wallet connect on the front, and call it a day. It’s the same old house edge, the same opaque math—just with a different deposit button.

Yoss.gg went the other way: make the simplest possible on-chain bet and make it actually fair.

Here’s how that works in practice:

  • P2P only. Every flip is between two players, never against a house. If you wager 10 USDC, your opponent wagers 10 USDC. That’s the whole pot.
  • Zero rake. The smart contract pays 20 USDC to the winner. There is no “tiny fee” or hidden margin baked into the odds.
  • Smart contract escrow. Funds move from wallets into a Base L2 contract, then straight back out to the winner. Yoss.gg never takes custody.
  • Commit-reveal randomness. Results are generated via commit-reveal, so neither side can front-run or peek at the outcome. You can verify it all on-chain.
  • USDC only, on Base. Using a stablecoin on a low-fee L2 keeps bets simple: no PnL from token volatility, and gas is ~1 cent per flip instead of eating the stake.

If you’re building in on-chain gaming, this kind of minimal primitive is underrated. One clean, provably fair coin flip that people actually trust is more powerful than a dozen “web3 casinos” that quietly lean on house edge.

Sometimes the honest version of a game isn’t more complicated. It’s just less extractive.

Google, Gemini’a geçişi kolaylaştıran iki yeni özellik duyurdu

Google Gemini

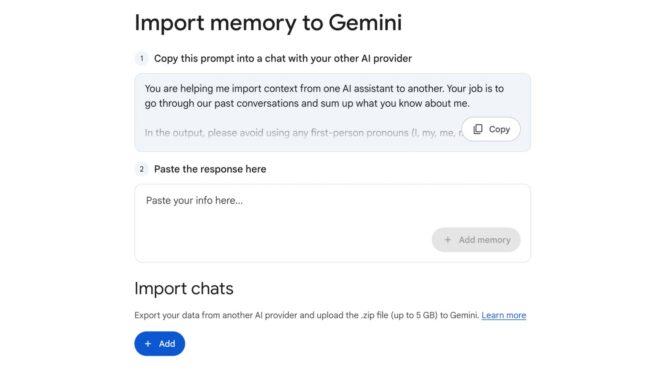
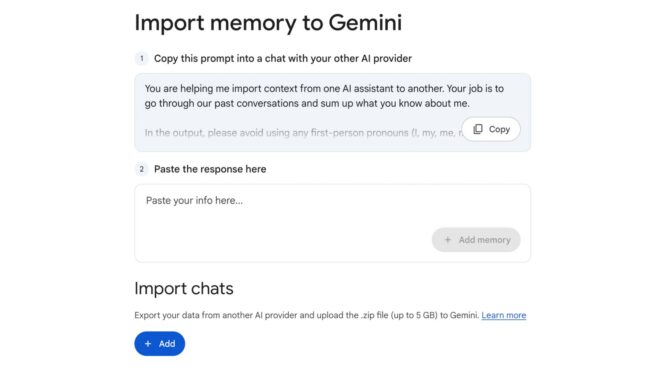
Google GeminiGoogle bugün Gemini’a geçişi kolaylaştıran iki faydalı özellik duyurdu. Kullanıcılar artık ChatGPT, Claude ya da Copilot gibi diğer yapay zeka sistemlerinde kayıt altına alınan kişisel bilgilerini kolaylıkla Gemini’a aktarabiliyor. Kullanılan mevcut sistemin, “Yapay zeka asistanları arasında bağlam aktarmama yardımcı oluyorsun. İşin, geçmiş konuşmalarımızı inceleyip hakkımda bildiklerini özetlemek.” prompt’una verdi cevabı analiz ederek yeni bir bellek oluşturan Gemini, bugün buna ek olarak sohbet geçmişini içe aktarma özelliğini de kazandı. Bu konuda yaptığı açıklamada, “Verilerinizi başka bir yapay zeka sağlayıcısından alarak (en fazla 5 GB) Gemini’a yükleyin.” diyen Google, burada .zip formatında yüklemeyi destekliyor. Anthropic de geçtiğimiz hafta Claude’a geçişi kolaylaştıran bir “bellek” özelliği sunmuştu. “Claude’a geçerken her şeye sıfırdan başlamayın.” denilerek duyurulan özellik, şirketin burada paylaştığı prompt’a diğer yapay zeka servislerinin verdiği yanıt temel alınarak çalışıyor. “Başka bir servise geçiyorum ve verilerimi dışa aktarmam gerekiyor. Hakkımda kaydettiğin her şeyi listele.” şeklinde başlayan prompt’a verilen cevabı analiz eden Claude, kullanıcı için yeni […]

Google, Gemini’a geçişi kolaylaştıran iki yeni özellik duyurdu yazısı ilk olarak Teknoloji haberleri – LOG üzerinde yayınlandı.

GDPR for US Companies: Does It Apply to You and What Do You Need to Do?

GDPR doesn’t care where your company is based. If you have visitors or customers in the EU, it applies to you — no matter how small your business.

The Short Answer

Yes. GDPR applies to any organization that processes personal data of people in the EU, regardless of where the company is located. This is Article 3 of the regulation — the territorial scope provision — and it was written this way deliberately.

If your website is accessible from Europe and you collect any data from EU visitors — analytics, email sign-ups, contact forms, session recordings — GDPR applies. The location of your servers doesn’t matter. Your company’s incorporation doesn’t matter. What matters is whether you’re processing personal data of EU residents.

“Personal data” is broad. It includes names, email addresses, IP addresses, cookie identifiers, and any information that can identify a specific person. If you’re running Google Analytics, you’re processing personal data of every visitor — including EU ones.

The “Establishment” vs “Targeting” Tests

GDPR reaches companies outside the EU through two distinct hooks.

The Establishment Test

If you have an office, subsidiary, branch, or any other stable arrangement in the EU, GDPR applies automatically. This covers companies that technically run operations from the US but have EU presences — even a single remote employee based in Germany could count, depending on context.

The Targeting Test

This is the one that catches most US businesses. If you offer goods or services to EU residents, or monitor their behavior, GDPR applies regardless of whether you have any EU presence at all.

Signs you’re targeting EU users:

  • Your site displays prices in Euros or GBP alongside USD
  • You run Google Ads campaigns targeting EU countries
  • You have EU-specific marketing campaigns or landing pages
  • You ship physical products to EU addresses
  • Your site is available in German, French, Spanish, or other EU languages
  • You have case studies or testimonials from EU customers

For the vast majority of US businesses with EU exposure, it’s the targeting test that applies. Running a SaaS product with a global sign-up page? You’re targeting EU users. Running an e-commerce store that ships internationally? You’re targeting EU users.

Even if you didn’t intend to target EU users, if they find your site, sign up, and you collect their data — you’re likely in scope.

What US Companies Often Get Wrong

“We’re too small to be targeted”

Size doesn’t determine whether GDPR applies to you — it affects enforcement likelihood, not legal obligation. A two-person startup with EU sign-ups is technically subject to GDPR. The practical risk is lower than for a company doing millions in EU revenue, but the legal exposure is real.

“GDPR only applies to EU companies”

This is the most common misconception. It’s also exactly what Article 3 was written to prevent. The drafters anticipated that companies would set up outside the EU to avoid the regulation. The extraterritorial scope closes that gap.

“We don’t have EU customers so it doesn’t apply”

Anonymous EU visitors may still count under some interpretations. If your analytics tool collects IP addresses from EU-based visitors and assigns them persistent cookie identifiers, you’re processing personal data — even if those visitors never became customers. The data subject doesn’t have to transact with you.

“We just need a cookie banner”

A cookie banner that says “we use cookies” and fires trackers before you click anything is not GDPR compliance. It’s a signal that you’ve heard of GDPR without implementing it. Compliance requires actual consent before non-essential cookies load, a privacy policy that discloses your real data practices, and a process for handling user rights requests.

What GDPR Actually Requires

If you’re a US company with EU visitors or customers, here’s what the regulation requires:

Lawful basis for processing. You need a legal justification for every category of personal data you collect. For marketing and analytics, this is usually consent. For contractual obligations (processing an order), it’s the contract. You must document your basis and disclose it.

Cookie consent before trackers fire. Non-essential cookies — analytics, advertising, retargeting pixels — cannot load until the visitor actively consents. Not a pre-ticked box. Not implied consent from continued browsing. An explicit opt-in that blocks the scripts until the visitor says yes.

Privacy policy disclosing EU user rights. Your privacy policy must explain: what data you collect, why, the legal basis for each purpose, which third parties you share it with (specific companies, not just “partners”), how long you retain it, and how EU visitors can exercise their rights — access, deletion, correction, portability, objection.

Ability to handle DSARs within 30 days. Any EU resident can request a copy of all personal data you hold on them, ask you to delete it, or tell you to stop processing it. You have 30 days to respond. You need a process for this before the first request lands — not a panicked scramble after.

Data processing agreements with your SaaS tools. If you use any third-party tool that processes EU visitor data on your behalf — email providers, analytics platforms, CRMs, support software — you need a Data Processing Agreement in place with each one. Most reputable SaaS tools have a DPA available; you often just need to sign it.

EU Representative Requirement

Article 27 of GDPR requires companies that are not established in the EU — but that regularly process EU personal data at scale — to designate a representative based in the EU. This representative acts as a point of contact for EU supervisory authorities and data subjects.

In practice, enforcement of this requirement against US-only companies is rare. There’s no US mechanism for EU regulators to compel appointment. Most small US businesses with incidental EU traffic ignore this requirement entirely, and regulators have not pursued it aggressively against small operators.

That said, if you’re doing meaningful EU revenue — hundreds of EU customers, regular EU marketing campaigns — it’s worth being aware of and discussing with a privacy lawyer. As EU-US enforcement mechanisms evolve, what’s practically ignored today may not be in five years.

The Risk Picture for US Companies

EU regulators can’t easily enforce against a US-only company that has no EU presence and no EU bank accounts. The practical enforcement path — serving notices, issuing fines, collecting — is genuinely difficult.

But the risk isn’t zero, and it scales with EU exposure:

EU-based customers can file complaints. A data subject complaint with a supervisory authority (like the German DPA or France’s CNIL) is a standard enforcement trigger. These authorities can investigate, make findings, and issue fines. For a US company with significant EU business, a complaint from a single unhappy customer can open a regulatory inquiry.

Compliance becomes a commercial requirement. If you want to sell to EU businesses — enterprises, government entities, regulated industries — they will ask about your GDPR compliance as part of procurement. Without it, you lose deals. This is often more immediately painful than regulatory risk.

Fines can include EU-sourced revenue. GDPR’s fine framework calculates maximum penalties as a percentage of global annual turnover. But regulators assessing actual fines consider EU revenue as a relevant factor. If you’re generating substantial EU revenue, the theoretical exposure is real.

The risk profile in summary: For a US-only business with incidental EU traffic, GDPR risk is low in practice. For a US company actively selling to EU customers, marketing to EU audiences, or building EU revenue, the risk is significant — both regulatory and commercial.

The 5 Things to Do First

If you’re a US company deciding where to start, this is the sequence that matters:

1. Run a scan to see what your site actually collects from EU visitors.
You can’t fix what you can’t see. A website scanner will show you every cookie, tracker, pixel, and third-party script firing on your site — including what fires before and after consent. Start here.

2. Add proper cookie consent.
Not a banner that loads everything and asks forgiveness. A consent mechanism that blocks non-essential scripts before consent is given, shows a clear accept/reject option, and logs consent for compliance records. Test it in incognito mode: if Google Analytics fires before you click “accept,” your consent is broken.

3. Update your privacy policy to disclose EU visitor rights.
Your privacy policy should describe what you collect from EU visitors, the legal basis for each use, which third-party tools process their data, and how they can exercise rights (access, deletion, correction). Most template privacy policies are inadequate. Use one generated from your actual data practices.

4. Get DPAs from your SaaS tools.
Go through every tool that processes visitor or customer data: your email platform, analytics provider, CRM, support software, payment processor. Find their DPA, sign it, and keep a record. Most major platforms (Google, HubSpot, Mailchimp, Stripe) have DPAs ready to sign — it takes minutes per tool.

5. Set up a DSAR process.
Create a simple intake method — a form, a dedicated email address — and assign someone to handle requests. Know where user data lives: your database, your email tool, your analytics platform, any backups. You have 30 days to respond. Building the process takes an afternoon; not having it when the first request lands costs much more.

Ready to see what your site is actually collecting from EU visitors?

Run a free scan at app.custodia-privacy.com/scan — no signup required. You’ll see every tracker, cookie, and third-party script loading on your site in under 60 seconds.

Last updated: March 2026

Apple, Mac Pro’yu resmi olarak emekliye ayırdı

Mac Pro

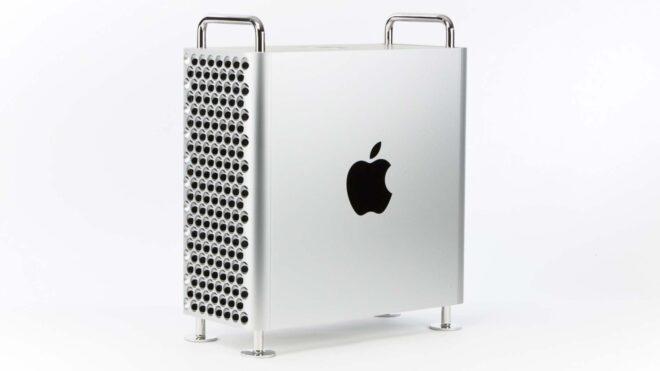
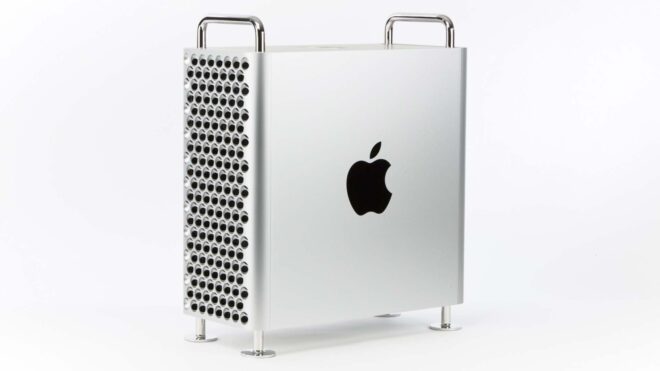
Mac ProDün gece sürpriz bir adım atan Apple, profesyonellere yönelik Mac Pro modelini resmi olarak emekliye ayırdı. 2023’te çıkan M2 Ultra işlemcili mevcut modeli satıştan kaldıran şirket, artık yeni bir Mac Pro’nun gelmeyeceğini duyurdu. Bu adım sonrasında Apple’ın masaüstü tarafındaki en güçlü Mac modeli Mac Studio olurken, cihazın yıl sonunda M5 Ultra ile güncellenmesi bekleniyor.

Apple, Mac Pro’yu resmi olarak emekliye ayırdı yazısı ilk olarak Teknoloji haberleri – LOG üzerinde yayınlandı.

Behind the Streams: Live at Netflix — 2025–10–22 Tokyo Video Tech #10 Session 2 Report

Most people know Netflix as the place you go to binge a series on a quiet evening. But since 2023, the company has been venturing into territory where there are no second takes — live streaming, at a scale that now reaches tens of millions of households simultaneously.

At Tokyo Video Tech #10 “Continuous”, held on October 22, 2025 at the Netflix Tokyo office, members of Netflix’s live streaming team gave their first talk in Tokyo. They walked the audience through what it actually takes to pull off a live broadcast at Netflix scale: the multi-path signal routing from venue to Broadcast Operations Center, the cloud encoding pipeline designed so that entire regions can fail without viewers noticing, and the culture of relentless rehearsal — including deliberate failure injection — that turns each one-shot event into something the team has already practiced dozens of times.

Report by: Katz Sakai

Launched in 2023, Netflix’s live streaming service has grown — through continuous trial and refinement — into a platform capable of reaching tens of millions of households simultaneously.
By skillfully building on the technical foundation and operational expertise developed through its VOD business, Netflix has created an architecture that balances the immediacy and reliability required for live broadcasting.
Above all, the session conveyed a clear message: success in live streaming depends on constant preparation and disciplined operational practice behind the scenes.

Live Streaming and Netflix

When people think of Netflix, on-demand streaming is usually what comes to mind.
However, the company has also been taking on the challenge of live streaming as a new form of entertainment.
Its first step in this direction was the Chris Rock: Selective Outrage comedy special, streamed live in 2023 — the first live event in Netflix’s history, which drew significant attention worldwide. Since then, Netflix has continued to scale its live streaming efforts.
For example, the boxing event Jake Paul vs. Mike Tyson was streamed live to more than 60 million households around the globe.

From the Venue to the BOC: Signal Aggregation

One of the biggest challenges in live streaming is ensuring that the video signals from the event venue are reliably delivered to the Broadcast Operations Center (BOC).

When Netflix first began its live streaming initiatives, all encoding was handled directly at the venue. However, due to various network and infrastructure constraints, achieving scalability proved difficult. Based on these lessons, Netflix transitioned to a model that minimizes on-site processing and consolidates control within the BOC.

Today, signals are transmitted from the venue to the BOC through multiple independent paths. Satellite links, dedicated lines, IP-based transmission (such as SRT), and bonded cellular connections — each with different technical characteristics — are combined to ensure that even if one path fails, the stream remains uninterrupted.
Furthermore, Netflix conducts technical studies for each transmission method, compiling the resulting insights into recommended parameters and operational guidelines that are shared with vendor partners.

At the BOC, the incoming signals are monitored and processed as needed.
This may include inserting the Netflix watermark, adding slates such as “Starting Soon” before the event or “Thanks for Watching” after it, and in the event of a total signal loss, displaying an emergency slate to maintain a consistent viewing experience.

For large-scale international events such as sports or entertainment broadcasts, the BOC also handles multilingual dubbing and audio mixing — producing simultaneous audio tracks in English, Japanese, German, and other languages to deliver regionally tailored streams to global audiences.

Converting BOC Signals into Delivery Formats in the Cloud

When transmitting video signals from the Broadcast Operations Center (BOC) to the cloud, Netflix places particular emphasis on redundancy and synchronization design to ensure uninterrupted streaming.
In live broadcasting, even a slight interruption can significantly impact the viewer experience, making it essential to balance both availability and consistency across the system.

For transmission from the BOC to the cloud, multiple independent paths — such as dedicated lines, IP-based links, and bonded cellular connections — are used in combination. This design ensures that if one route encounters a failure, others can immediately take over.
Within the cloud, the same incoming signal is processed simultaneously across multiple regions, preventing any single point of failure and ensuring high resilience.

Once the signals reach the cloud, they are first processed by encoders and then passed to live packagers, which convert them into delivery-ready formats.
These packagers leverage Netflix’s extensive knowledge accumulated through years of VOD delivery — specifically, its database of device-level capabilities and limitations. In practice, this means the system already “knows” which codecs, resolutions, and streaming formats are supported on each device, and applies that intelligence directly to live packaging.
As a result, Netflix minimizes compatibility risks and ensures that live streams maintain consistent quality and playback success rates across the vast range of viewing devices.

The packagers are also designed to handle the precise timing and segment synchronization requirements unique to live streaming.
All cloud encoders reference a shared epoch (a common timing source), ensuring that segments generated in different regions remain interchangeable. This enables instant failover between regions — if one region experiences an outage, another can seamlessly take over without disrupting the live stream.

In this way, Netflix’s live streaming architecture — built on the three design pillars of redundancy, time synchronization, and device compatibility — maintains high reliability while delivering a consistent playback experience across diverse devices worldwide.

Principles of Delivery: Compatibility, Scale, and Quality

The three key elements that Netflix prioritizes in live delivery are compatibility, scale, and quality.

Compatibility
The devices used by Netflix viewers are incredibly diverse — from smartphones released many years ago to the latest high-end devices — representing thousands of playback environments. As with VOD, Netflix’s live streaming platform is designed with the guiding principle of being playable on as many devices as possible.
To achieve this, the delivery protocol is unified under an HTTPS-based approach, allowing existing Netflix players to stream live content without modification.
Video is encoded in both the widely compatible AVC (H.264) and the more efficient HEVC (H.265) formats, while support for the next-generation AV1 codec continues to expand. This approach ensures that older devices can still play streams smoothly, while newer ones benefit from higher picture quality — achieving a balance between inclusivity and performance.

Scale
Live streaming can attract tens of millions of concurrent viewers accessing the service simultaneously. To handle this immense load, Netflix leverages its proprietary CDN, Open Connect. More than 18,000 servers deployed across 6,000 locations worldwide receive live segments from the origin and deliver them to viewers from the nearest node.
The player references manifests built on a segment template model, minimizing server queries and allowing efficient handling of massive request volumes.
This scalable architecture enables stable delivery even during global events such as Jake Paul vs. Mike Tyson.

Quality
Just as in VOD, the Netflix player continuously monitors network conditions to select the optimal bitrate in real time. If throughput drops during playback, the system immediately switches to an alternative CDN node or adjusts the video bitrate to prevent buffering. Through these adaptive measures, Netflix ensures that viewers around the world can enjoy a smooth, uninterrupted live streaming experience regardless of their network conditions.

Success in Live Streaming Starts with Preparation

Another crucial factor in live streaming is preparation and operational discipline. Unlike VOD, live streaming is a true one-shot performance — there are no retakes. For that reason, the team treats preparation like daily “training,” continuously running tests and rehearsals to stay ready for any scenario.

Building robust test environments
To simulate real-world live events, Netflix developed an internal system capable of generating virtual live streams. This system allows engineers to instantly launch test broadcasts and verify the entire pipeline — from encoding and packaging to CDN behavior — under production-like conditions. It enables safe experimentation with new features and architectural changes without risking live operations.

Practicing resilience through failure testing
Netflix routinely performs failure injection tests, deliberately introducing issues such as network latency, packet loss, and simulated cloud region outages. This culture of anticipating the unexpected strengthens system robustness, ensuring that even during large-scale global events, live streams remain stable and uninterrupted.

Forecasting and real-time adaptability
Every live event begins with audience size predictions powered by machine learning models, allowing teams to pre-provision sufficient cloud and CDN resources. During and immediately before broadcasts, Netflix continuously analyzes real-time viewership trends. If the system detects audience growth exceeding expectations, capacity adjustments are made on the fly to prevent congestion. By integrating thorough pre-event simulations with agile real-time responses, Netflix achieves stable and consistent live delivery under any conditions.

In Conclusion

What stood out most in this session was how Netflix approaches live streaming — a relatively new domain for the company — without relying on individual know-how. Instead, the team has established clearly documented procedures and specifications to ensure operational consistency and reproducibility. Even the signal setup from the venue to the Broadcast Operations Center (BOC) has been systematized into operational guidelines rather than being treated as a “black magic”, enabling the same level of quality and reliability across different countries and production environments.

Equally impressive was how Netflix has effectively leveraged its long-standing technical assets and operational expertise from VOD streaming. By applying its accumulated knowledge of device compatibility and CDN scaling directly to live workflows, the company delivers live events with the same “Netflix-quality” scalability and reliability that define its on-demand service.

Above all, the session conveyed a powerful message: live success is built on daily preparation. Through continuous testing in virtual live environments, deliberate failure injections, and regular rehearsals, Netflix ensures that each one-time broadcast runs smoothly when it matters most.

For more details on Netflix’s live streaming technology and engineering practices, you can refer to their official Netflix Tech Blog.

Join Us

Tokyo Video Tech is an open community — whether you’re a seasoned video engineer or just curious about the field, you’re welcome to join. Follow us on Luma to stay updated on upcoming events.
→ Join the mettup