Quick Verdict


SonarQube is the stronger platform in nearly every dimension that matters for code quality analysis in 2026. SonarQube provides 6,500+ deterministic analysis rules across 35+ languages, the most mature quality gate enforcement system in the market, self-hosted deployment options (including a free Community Build), security scanning with taint analysis, and technical debt tracking with remediation time estimates. Code Climate provides maintainability grading (A-F scores), test coverage tracking, and basic PR feedback through a lightweight cloud-only platform. The gap between these two tools has widened significantly as SonarQube has added AI features, security scanning, and cloud hosting while Code Climate’s investment has slowed following the sunset of its Velocity engineering metrics product.
Choose SonarQube if: you want the deepest code quality analysis available, need self-hosted deployment for data sovereignty, require security scanning alongside quality analysis, want enterprise quality gate enforcement, or need support for legacy languages like COBOL and ABAP. SonarQube is the better choice for teams of every size – its free Community Build and Cloud Free tier provide more value than Code Climate’s paid plans.
Choose Code Climate if: you specifically need A-F maintainability grading for a small team, want the absolute simplest setup with zero pipeline configuration, and do not need security scanning, deep rule coverage, or self-hosted deployment. Code Climate remains a functional tool for lightweight code quality monitoring, but it no longer competes with SonarQube on depth, breadth, or value.
If you are evaluating both tools today: Start with SonarQube Cloud Free (50K LOC, branch and PR analysis, zero cost). It provides deeper analysis than Code Climate’s paid plans at no charge. If you need more than 50K LOC or self-hosted deployment, the SonarQube Community Build is free and open source. The practical case for choosing Code Climate over SonarQube is very narrow in 2026.
At-a-Glance Comparison
| Category |
SonarQube |
Code Climate |
| Primary focus |
Code quality + security |
Maintainability metrics |
| Analysis rules |
6,500+ deterministic rules across 35+ languages |
Embedded engines covering ~30 languages |
| Quality gates |
Best-in-class enforcement with configurable conditions |
Basic PR status checks for maintainability/coverage |
| Technical debt tracking |
Remediation time estimates + trend charts |
Maintainability grades (A-F) |
| Security scanning (SAST) |
Yes – taint analysis in Developer+ editions |
No |
| SCA (dependency scanning) |
Advanced Security add-on (Enterprise) |
No |
| Secrets detection |
Yes (400+ patterns) |
No |
| Code coverage |
Yes |
Yes |
| Duplication detection |
Yes (with percentage metrics) |
Yes |
| AI features |
AI CodeFix, AI Code Assurance |
None |
| IDE integration |
SonarLint (VS Code, JetBrains, Eclipse, Visual Studio) |
None |
| Git platforms |
GitHub, GitLab, Bitbucket, Azure DevOps |
GitHub, GitLab, Bitbucket |
| Self-hosted |
Core offering (Community Build is free) |
No – cloud only |
| Free tier |
Community Build (self-hosted) + Cloud Free (50K LOC) |
Open-source repos only |
| Starting paid price |
EUR 30/month (Cloud Team) or ~$2,500/year (Server Developer) |
~$15/user/month |
| Pricing model |
Lines of code (Server) or LOC tiers (Cloud) |
Per active user |
| Setup time |
Minutes (Cloud) to full day (self-hosted Server) |
Under 10 minutes |
| User base |
7M+ developers, 400K+ orgs |
Declining – founding team moved to Qlty |
What Is SonarQube?
SonarQube is a code quality and security analysis platform developed by SonarSource, a Swiss company founded in 2008. It is the most widely adopted static analysis platform in the industry, used by over 7 million developers across 400,000+ organizations. The platform provides 6,500+ analysis rules covering bugs, code smells, security vulnerabilities, and security hotspots across 35+ languages.
SonarQube is available in multiple deployment options: SonarQube Server (self-hosted, with Community Build free and open source, plus Developer, Enterprise, and Data Center commercial editions) and SonarQube Cloud (managed SaaS, with a Free tier supporting 50K LOC). The platform’s defining feature is quality gate enforcement – automated conditions that block code from being merged when it fails defined quality thresholds. This enforcement mechanism is consistently cited as SonarQube’s most valuable feature because it turns code quality from a suggestion into a requirement.
SonarLint, the free IDE plugin for VS Code, JetBrains IDEs, Eclipse, and Visual Studio, extends the platform into the developer’s editor. In connected mode, SonarLint synchronizes team quality rules so that what developers see in their IDE matches exactly what the CI pipeline enforces.
What Is Code Climate?
Code Climate Quality is a cloud-based code analysis platform that focuses on maintainability metrics. It assigns A-F grades to files and repositories based on complexity, duplication, and structural issues, tracks test coverage percentages, and provides PR-level feedback through GitHub, GitLab, and Bitbucket integrations.
Code Climate originally offered two products: Quality (code analysis) and Velocity (engineering metrics tracking DORA metrics, cycle time, and team throughput). Velocity was sunset, and the founding team moved on to build Qlty, a new code quality platform. The Quality product remains operational but has received notably less investment compared to competitors.
Code Climate Quality is cloud-only with no self-hosted option. It supports approximately 30 languages through embedded analysis engines. Paid plans for private repositories start at approximately $15/user/month, with free access for public open-source projects.
Code Quality Analysis
Rule Engine Depth
This is the dimension where the gap between SonarQube and Code Climate is widest, and it is not close.
SonarQube’s rule engine contains over 6,500 deterministic rules with language-specific rule sets that go remarkably deep. Java alone has over 900 rules covering null pointer dereferences, resource leaks, thread safety violations, incorrect API usage, and hundreds of other patterns. Python, JavaScript/TypeScript, C#, C++, and Go each have similarly deep rule sets. Every rule is documented with compliant and non-compliant code examples, remediation guidance, and severity classification. The rules are not generic pattern matches – they are language-specific analysis that understands the idioms, conventions, and common pitfalls of each ecosystem.
Code Climate Quality runs a set of embedded analysis engines – tools like ESLint, RuboCop, Pylint, and others – wrapped in a unified interface. The platform focuses on structural maintainability issues: complexity (particularly cyclomatic complexity), duplication, file length, method length, and similar metrics. This is a narrower scope than SonarQube’s comprehensive analysis. Code Climate does not detect bugs, security vulnerabilities, resource leaks, thread safety violations, or framework-specific anti-patterns. Its analysis is limited to maintainability concerns.
The practical impact: SonarQube catches both the maintainability issues that Code Climate detects and thousands of additional bug patterns, security vulnerabilities, and language-specific anti-patterns that Code Climate cannot detect. Teams that switch from Code Climate to SonarQube consistently report finding significant issues in their codebases that Code Climate never flagged – including real bugs that were causing production incidents.
Quality Gates
Quality gates are arguably SonarQube’s most important feature and a capability where Code Climate falls far behind.
SonarQube’s quality gates define conditions that code must meet before it can be merged or deployed. Typical conditions include minimum code coverage percentage on new code, zero new bugs above a severity threshold, duplication below a percentage limit, and technical debt ratio within acceptable bounds. When a pull request fails the quality gate, SonarQube blocks the merge and posts the failing conditions directly in the PR through PR decoration on GitHub, GitLab, Bitbucket, or Azure DevOps. In GitHub, teams configure branch protection rules to require the SonarQube quality gate to pass, creating an automated enforcement mechanism that prevents code quality from degrading over time.
The implementation is highly configurable. Quality gates can be applied per-project or across portfolios, conditions can target new code only (the “Clean as You Code” methodology), and the enforcement is deterministic – there is no ambiguity about whether code passes or fails. Engineering managers consistently cite quality gates as the feature that delivers the most long-term value because they create a behavioral feedback loop: developers write cleaner code proactively because they know the gate will catch problems.
Code Climate provides basic PR status checks that can report whether a PR introduces new maintainability issues or drops below a coverage threshold. These checks can be configured as required in GitHub’s branch protection rules. However, the sophistication and granularity do not approach SonarQube’s. Code Climate cannot enforce conditions on new bugs (it does not detect bugs), security vulnerabilities (it does not scan for them), or technical debt ratio (it does not quantify debt in remediation hours). The quality enforcement is limited to maintainability grades and coverage percentages.
Bottom line: If quality gate enforcement is a priority – and for most engineering organizations it should be – SonarQube’s gates are in a different league than Code Climate’s basic PR checks.
Technical Debt Tracking
SonarQube quantifies technical debt as estimated remediation time – the total hours required to fix all identified issues. This metric is tracked over time and broken down by project, module, language, and severity. The trend charts on the dashboard show whether your codebase is improving or degrading, making technical debt management a data-driven process. The Enterprise Edition adds portfolio management that aggregates technical debt across multiple projects, providing executive-level visibility into organizational code health. For engineering managers who need to report metrics to leadership, this capability is difficult to replicate with any other tool.
Code Climate takes a different approach to technical debt. It assigns maintainability grades (A through F) to files and repositories based on complexity, duplication, and structural issues. The grades are intuitive and easy to communicate – “this file is a D” is immediately understandable. However, the grading system lacks the quantitative precision of SonarQube’s remediation time estimates. Code Climate cannot answer “how many engineering hours would it take to fix our technical debt” with a concrete number. It can tell you which files are problematic, but not the effort required to fix them.
The practical difference: SonarQube provides a quantified, actionable view of technical debt that connects directly to engineering capacity planning. Code Climate provides a qualitative view that is useful for identifying problematic areas but does not translate into actionable resource allocation. Teams that need to make business cases for refactoring investments need SonarQube’s numbers, not Code Climate’s letter grades.
Code Coverage and Duplication
Both tools track code coverage and detect duplication, and the basic capabilities are broadly comparable.
SonarQube displays coverage metrics on the project dashboard, tracks coverage trends over time, and enforces minimum coverage on new code through quality gates. It parses coverage reports from most common testing frameworks and supports both line coverage and condition coverage. The coverage data integrates directly into quality gate conditions, meaning PRs can be blocked when coverage on new code drops below the team’s threshold.
Code Climate similarly tracks coverage percentages and integrates with standard coverage report formats. Coverage data appears in PR status checks and on the repository dashboard. The coverage tracking is one of Code Climate’s stronger features and is comparable to SonarQube’s basic coverage reporting.
For duplication detection, both tools identify copy-paste code. SonarQube provides a duplication percentage metric, highlights specific duplicated blocks, and tracks duplication trends. Code Climate also detects duplication as part of its maintainability analysis.
The meaningful difference is that SonarQube’s coverage analysis includes condition coverage (not just line coverage), correlates coverage gaps with complexity hotspots, and presents this data in the context of quality gate enforcement and technical debt remediation estimates. Code Climate’s coverage tracking is more straightforward – it shows the metrics but does not connect them to the broader quality enforcement framework that SonarQube provides.
Security Scanning
SAST Capabilities
This is an area where SonarQube has a commanding advantage because Code Climate does not offer security scanning at all.
SonarQube’s security rules cover OWASP Top 10, CWE Top 25, and SANS Top 25 vulnerability categories. Approximately 15% of its 6,500+ rules are security-focused, which translates to roughly 1,000 security rules – a substantial number. The Developer Edition and above include taint analysis, which tracks the flow of data through the application to detect injection vulnerabilities that span multiple methods or classes. This is critical for catching SQL injection, XSS, and other injection attacks where tainted input enters the application in one function and reaches a dangerous sink several layers deeper.
Code Climate Quality does not include any security scanning capabilities. It does not detect SQL injection, XSS, authentication issues, cryptographic weaknesses, insecure data handling, or any other security vulnerability class. Organizations using Code Climate for code quality must add a separate security tool – Semgrep, Snyk Code, Checkmarx, or another SAST product – to cover security.
The security gap is significant. SonarQube provides both code quality and security analysis in a single platform. Code Climate provides only code quality analysis (and a narrower version of it). For teams that need any security scanning alongside their quality analysis, SonarQube eliminates the need for a separate security vendor.
SCA, Secrets Detection, and SBOM
SonarQube’s security capabilities extend beyond SAST. The platform detects 400+ secret patterns – API keys, database passwords, authentication tokens, and private certificates – and surfaces these findings in pull requests to prevent secrets from being merged. The Enterprise Edition’s Advanced Security add-on provides SCA (Software Composition Analysis) for dependency vulnerability scanning, malicious package detection, license compliance checking, and SBOM generation in CycloneDX and SPDX formats.
Code Climate offers none of these capabilities. No secrets detection, no dependency scanning, no SBOM generation. Teams using Code Climate need separate tools for every security dimension.
Self-Hosted vs Cloud-Only Deployment
SonarQube: Self-Hosted as a Core Strength
Self-hosted deployment is fundamental to SonarQube’s value proposition and one of its most important differentiators from Code Climate.
The Community Build is free and open source, allowing any organization to deploy a SonarQube server on their own infrastructure. The only external requirement is a PostgreSQL database. Commercial editions (Developer, Enterprise, Data Center) add features while maintaining the self-hosted model. The Data Center Edition provides high availability with horizontal scaling for mission-critical deployments.
For organizations in regulated industries – government, defense, financial services, healthcare – the ability to keep all code and analysis data within their own network is often a non-negotiable requirement. SonarQube has been meeting this requirement for over a decade, with battle-tested deployment patterns, extensive documentation, and a large community of self-hosted users. Air-gapped deployments are fully supported.
SonarQube Cloud (formerly SonarCloud) provides the managed SaaS alternative for teams that do not need self-hosted infrastructure. The analysis engine is the same, and SonarQube Cloud typically receives new features before the Server editions. The Free tier supports 50K LOC with branch and PR analysis.
Code Climate: Cloud Only
Code Climate is entirely cloud-based with no self-hosted deployment option. All code analysis runs on Code Climate’s cloud infrastructure. There is no on-premises edition, no Docker deployment, and no way to keep code within your own network.
This is a hard constraint for any organization with data sovereignty requirements. If your compliance policies prohibit sending source code to third-party cloud services, Code Climate is not an option. This eliminates Code Climate from consideration for government agencies, defense contractors, most financial institutions, and many healthcare organizations.
The deployment gap matters beyond compliance. Even for teams without strict data sovereignty requirements, self-hosted deployment provides advantages: no dependency on a third-party service for a critical part of your development workflow, the ability to customize and scale infrastructure independently, and protection against vendor pricing changes or service discontinuation. Given the uncertainty around Code Climate’s future investment (the founding team has moved to Qlty), self-hosted SonarQube provides an additional layer of continuity that cloud-only Code Climate cannot match.
Language and Framework Support
Breadth and Depth of Coverage
SonarQube supports 35+ languages in its commercial editions and 20+ in the free Community Build. The language list includes all mainstream languages (JavaScript, TypeScript, Python, Java, C#, Go, PHP, Ruby, Kotlin, Swift, Rust, C, C++) plus legacy enterprise languages that Code Climate does not support – COBOL, ABAP, PL/SQL, PL/I, RPG, and VB6. These legacy languages are only available in the Enterprise Edition ($20,000+/year), but for organizations maintaining legacy codebases, SonarQube may be the only commercial tool that provides analysis for them.
Code Climate supports approximately 30 languages through its embedded analysis engines. The list covers mainstream languages adequately but lacks the legacy enterprise language support and the depth of analysis per language that SonarQube provides.
Analysis Depth Per Language
The raw language count comparison is misleading because SonarQube’s analysis depth per language is substantially greater. Java has 900+ rules in SonarQube covering everything from basic null checks to complex thread safety patterns, resource leak detection across try-catch-finally blocks, and framework-specific rules for Spring, JEE, and other frameworks. Python, JavaScript/TypeScript, C#, and C++ have similarly deep rule sets with hundreds of language-specific rules each.
Code Climate’s per-language analysis focuses on structural metrics – complexity, duplication, file and method length. It does not have language-specific bug detection rules, framework-specific anti-pattern detection, or the kind of deep data flow analysis that catches subtle issues. The difference between “this method is too complex” (Code Climate) and “this method has a resource leak that only manifests when the database connection fails during a retry” (SonarQube) is the difference between a metrics tool and a deep static analyzer.
Framework-Specific Analysis
SonarQube provides framework-specific rules for Spring Boot, JEE, Django, Flask, React, Angular, ASP.NET, and other popular frameworks. These rules catch framework-specific anti-patterns, misconfigurations, and performance issues that generic metrics cannot detect.
Code Climate does not offer framework-specific analysis. Its embedded engines apply generic structural rules regardless of the framework being used.
Infrastructure as Code
SonarQube’s Community Build includes IaC analysis for Terraform, Kubernetes, Docker, and CloudFormation configurations. These rules catch common misconfigurations and security issues in infrastructure definitions. Code Climate does not analyze infrastructure-as-code files.
PR Integration and Developer Experience
Pull Request Feedback
SonarQube posts quality gate status (pass/fail) along with a summary of new issues, coverage changes, and duplication changes directly in pull requests. In GitHub, the quality gate status can be configured as a required check through branch protection rules, creating a hard block on merging non-compliant code. Individual findings link to detailed rule documentation with compliant and non-compliant code examples and remediation guidance. The feedback is comprehensive and actionable.
Code Climate posts maintainability analysis results in pull requests, showing which files have decreased in maintainability grade and highlighting new complexity or duplication issues. Coverage status is reported as a separate check. The feedback is clean and easy to understand but covers a narrower range of issues than SonarQube’s comprehensive quality gate summary.
Both tools support GitHub, GitLab, and Bitbucket for PR integration. SonarQube additionally supports Azure DevOps, which Code Climate does not.
IDE Integration
SonarQube’s IDE integration through SonarLint is one of the best IDE experiences in the static analysis category and a major advantage over Code Climate.
SonarLint is a free plugin available for VS Code, JetBrains IDEs (IntelliJ, WebStorm, PyCharm, and others), Eclipse, and Visual Studio. It runs analysis rules in real time as developers write code. The connected mode feature synchronizes team Quality Profiles so that what developers see in their IDE matches exactly what the CI pipeline enforces. This eliminates the cycle of pushing code, waiting for CI, finding issues, and pushing fixes. Issues are caught before code is even committed.
Code Climate does not offer any IDE integration. Developers only receive feedback after pushing code and opening a PR. There is no way to catch Code Climate’s maintainability issues during the coding phase. This means the feedback loop is significantly longer than SonarQube’s, and developers waste more time on issues that could have been caught earlier.
The IDE gap is substantial. SonarLint’s connected mode is genuinely one of the most effective shift-left mechanisms available in any code quality tool. Code Climate’s complete absence of IDE integration is a meaningful disadvantage for teams that want to catch issues at the earliest possible point.
Setup and Onboarding
Code Climate’s setup experience is faster and simpler for cloud-based analysis. Connect your GitHub, GitLab, or Bitbucket account, select repositories, and analysis begins automatically. Total time from signup to first results is under 10 minutes with no CI/CD configuration required.
SonarQube Cloud setup is reasonably straightforward – connect your Git platform account, configure the SonarScanner in your CI/CD pipeline, and analysis begins running. Total time is 30 minutes to a few hours depending on build system complexity. SonarQube Server (self-hosted) setup is more involved – provisioning a database, deploying the server, configuring authentication, installing the scanner, and tuning JVM settings. Total time is typically a full day of DevOps effort.
For teams that want to be running within minutes, Code Climate has an edge in initial setup. But this advantage is a one-time benefit that is quickly overshadowed by SonarQube’s deeper analysis, better quality gates, and IDE integration. SonarQube Cloud Free provides a setup experience that approaches Code Climate’s simplicity while delivering substantially more value.
CI/CD Integration
Pipeline Configuration
Code Climate’s analysis runs automatically when code is pushed – no CI/CD pipeline configuration is required for the core maintainability analysis. Coverage reporting requires CI/CD integration to upload test coverage data, but the structural analysis is pipeline-less. This simplicity is Code Climate’s strongest operational advantage.
SonarQube requires scanner configuration in the CI/CD pipeline. For SonarQube Cloud, teams add the SonarScanner to their CI/CD workflow. For SonarQube Server, the setup involves configuring the scanner, setting project keys, and establishing authentication between the CI runner and the SonarQube server. SonarSource provides official integrations for GitHub Actions, GitLab CI, Azure Pipelines, Jenkins, Maven, Gradle, and .NET, which streamlines the process.
The tradeoff is control versus convenience. SonarQube’s explicit CI/CD integration gives teams precise control over when analysis runs, what code is scanned, and how results are reported. Code Climate’s implicit integration is faster to set up but offers less fine-grained control over the analysis workflow.
Build System Support
SonarQube has broader build system integration through dedicated plugins for Maven, Gradle, .NET/MSBuild, and Ant, plus a standalone CLI scanner for other environments. The ecosystem is extensive and well-documented after over a decade of development.
Code Climate supports standard CI/CD platforms for coverage upload but does not offer the same depth of build-system-specific plugins. For teams with complex build systems – particularly Java projects using Maven or Gradle, or .NET projects using MSBuild – SonarQube’s native plugins provide a smoother integration experience.
AI Features
SonarQube’s AI Capabilities
SonarQube has invested in AI features that Code Climate has not matched.
AI CodeFix generates remediation suggestions when the analysis engine identifies an issue. The suggestions are functional for straightforward issues like null check additions, resource cleanup, and simple refactoring. While AI CodeFix does not match the contextual depth of AI-native tools like CodeRabbit, it provides a meaningful productivity boost for common issue patterns.
AI Code Assurance automatically detects code generated by AI coding assistants like GitHub Copilot, applies enhanced verification rules to that code, and provides a real-time quality status for projects containing AI-generated code. SonarSource reports that teams using AI Code Assurance are 24% more likely to report lower vulnerability rates and 20% more likely to report lower defect rates from AI-generated code.
Code Climate’s AI Capabilities
Code Climate does not offer any AI-powered features. No AI-assisted remediation, no AI code detection, no AI-powered review. In a market where AI-generated code is becoming a significant portion of new code (30-70% in many organizations), Code Climate’s lack of AI governance features is a growing gap.
The AI gap will widen. As AI coding assistants become standard development tools, the ability to verify and govern AI-generated code becomes increasingly important. SonarQube is investing in this area. Code Climate is not.
Pricing Breakdown
SonarQube Pricing
| Plan |
Price |
What You Get |
| Community Build (self-hosted) |
Free |
Open source, 20+ languages, basic quality gates, no branch/PR analysis |
| Cloud Free |
Free |
Up to 50K LOC, 30 languages, branch/PR analysis, GitHub/GitLab/Bitbucket/Azure DevOps |
| Cloud Team |
From EUR 30/month |
Up to 100K LOC at base, full branch/PR analysis, quality gates on PRs, SonarLint connected mode |
| Developer Edition (Server) |
From ~$2,500/year |
35+ languages, branch/PR analysis, PR decoration, secrets detection, taint analysis |
| Enterprise Edition (Server) |
From ~$20,000/year |
Portfolio management, security reports, COBOL/ABAP/PL/SQL, Advanced Security add-on available |
| Data Center Edition (Server) |
Custom |
High availability, horizontal scaling, component redundancy |
Code Climate Pricing
| Plan |
Price |
What You Get |
| Open Source |
Free |
Public repos only, maintainability analysis, coverage tracking |
| Paid (Private Repos) |
~$15/user/month |
Private repo analysis, maintainability grades, coverage tracking, PR feedback |
Side-by-Side Cost at Scale
| Team Size |
SonarQube Cost (Annual) |
Code Climate Cost (Annual) |
Notes |
| 1-3 devs (side project) |
Free (Cloud Free or Community) |
Free (open source only) or ~$576+ |
SonarQube free tiers cover private repos |
| 5 devs (startup) |
Free (Cloud Free or Community) |
~$900 |
SonarQube is free and provides deeper analysis |
| 10 devs (100K LOC) |
~$384 (Cloud Team) or ~$2,500 (Developer Server) |
~$1,800 |
SonarQube Cloud Team is cheaper and deeper |
| 20 devs (500K LOC) |
~$2,500 (Developer Server) |
~$3,600 |
SonarQube is cheaper with much deeper analysis |
| 50 devs (2M LOC) |
~$10,000 (Developer Server) |
~$9,000 |
Similar cost, but SonarQube includes security scanning |
| 100 devs (5M LOC) |
~$35,000 (Enterprise Server) |
~$18,000 |
SonarQube costs more but adds security, compliance, legacy languages |
Key Pricing Observations
SonarQube’s free tiers are dramatically more useful. The Community Build gives you a full self-hosted static analysis server with 20+ language support at zero cost. Cloud Free gives you 50K LOC with branch and PR analysis. Code Climate’s free tier is limited to public open-source repositories – teams with private codebases get nothing for free. For any team evaluating these tools, starting with SonarQube’s free options is the obvious first step.
SonarQube provides more value per dollar at every price point. At $2,500/year for the Developer Edition, SonarQube gives you 6,500+ rules, security scanning with taint analysis, quality gate enforcement, SonarLint connected mode, and self-hosted deployment. At $1,800/year (10 developers), Code Climate gives you maintainability grades, coverage tracking, and basic PR feedback. The depth-per-dollar ratio strongly favors SonarQube.
Code Climate’s per-user pricing is more predictable. SonarQube Server editions are priced by lines of code, which means costs grow with your codebase even if your team size stays the same. Code Climate’s per-user model provides predictable costs as codebases grow. However, this predictability advantage is less meaningful when SonarQube provides substantially more capability at each price point.
The hidden cost of SonarQube is operations. Self-hosted SonarQube Server requires a database, JVM tuning, upgrade management, and ongoing monitoring. Even if the license is cheaper, the DevOps hours required for maintenance add to the effective cost. SonarQube Cloud eliminates this overhead. Code Climate also eliminates this overhead as a fully managed cloud platform. For teams without dedicated DevOps resources, SonarQube Cloud or Code Climate’s cloud-only model avoids operational burden.
At 50+ developers, the comparison shifts. SonarQube’s LOC-based pricing can exceed Code Climate’s per-user pricing at large team sizes with large codebases. However, at this scale, teams are typically choosing between SonarQube Enterprise (with security scanning, compliance reporting, and portfolio management) and Code Climate (with only maintainability grading). The feature gap at enterprise scale makes raw price comparison misleading – SonarQube’s higher cost buys substantially more capability.
Technical Debt Management
SonarQube’s Quantified Approach
SonarQube treats technical debt as a measurable, trackable metric. Every issue detected by the analysis engine carries an estimated remediation time – the hours required to fix it. These estimates are aggregated into a total technical debt figure for each project, tracked over time on trend charts, and broken down by severity, category, and language.
The “Clean as You Code” methodology focuses quality gates on new code only, accepting existing debt while preventing new debt from being introduced. This approach is pragmatic for teams with large legacy codebases – you do not have to fix everything at once, but every new PR must meet the quality standard. Over time, as code is modified and rewritten, the overall debt naturally decreases.
The Enterprise Edition adds portfolio management that aggregates technical debt across multiple projects. Engineering directors can see which projects carry the most debt, which are improving, and which are degrading. This organizational view makes technical debt a discussion item in engineering leadership meetings with concrete numbers rather than vague impressions.
Code Climate’s Grade-Based Approach
Code Climate assigns maintainability grades (A through F) based on structural metrics – complexity, duplication, file length, and method length. The grades are intuitive and easy to communicate. An executive can understand “40% of our files are rated C or below” without needing to understand remediation hours or debt ratios.
However, the grading system lacks actionable precision. A file rated “D” could take 30 minutes to improve or 3 days – the grade does not distinguish. You cannot aggregate grades into a meaningful portfolio view the way you can aggregate remediation hours. And the grades do not connect to engineering capacity planning – knowing that a file is a D does not tell you how to prioritize it against a C in another project.
For engineering leadership: SonarQube’s remediation time estimates provide the data needed to make resource allocation decisions. Code Climate’s grades provide a high-level health indicator but not the quantitative foundation for planning.
Dashboard and Reporting
SonarQube’s Comprehensive Dashboards
SonarQube’s project-level dashboards show quality ratings (A through E for each dimension), technical debt in hours, coverage percentage, duplication percentage, and security hotspot counts. Trend charts show how these metrics change over time. Drill-down views let you explore issues by severity, category, file, and language.
The Enterprise Edition adds portfolio management that aggregates metrics across multiple projects plus security compliance reports aligned to OWASP and CWE standards. Executive dashboards summarize organizational code health for leadership presentations. These reporting capabilities are essential for organizations that need to demonstrate compliance or justify engineering investments.
Code Climate’s Simpler Dashboards
Code Climate’s dashboards provide repository-level views of maintainability grades, test coverage percentages, and issue trends. The interface is clean and the maintainability grades provide a quick visual indicator of code health. However, the dashboards lack the depth of SonarQube’s technical debt quantification, portfolio-level aggregation, security-specific views, and compliance reporting.
For small teams that need a quick overview of code health, Code Climate’s dashboards are adequate. For organizations that need detailed reporting, compliance documentation, or portfolio-level visibility, SonarQube’s dashboards are substantially more capable.
When to Choose SonarQube
Enterprise engineering organizations with quality standards. SonarQube’s 6,500+ rules and quality gate enforcement are unmatched. The depth of analysis per language catches subtle bugs, resource leaks, and security issues that Code Climate cannot detect. If your organization needs to enforce minimum quality standards consistently across multiple teams and projects, SonarQube’s enforcement mechanism is proven at scale.
Teams that need self-hosted deployment. If data sovereignty is a requirement – code and analysis data must stay within your network – SonarQube is the clear choice. The free Community Build alone provides a self-hosted static analysis server that is more capable than Code Climate’s paid offering. Code Climate has no self-hosted option.
Organizations that need security scanning. SonarQube provides SAST with taint analysis, secrets detection, and (in Enterprise) SCA with SBOM generation. Code Climate provides no security scanning. Any team that needs security alongside quality analysis should choose SonarQube to avoid adding a separate security vendor.
Teams with diverse or legacy tech stacks. SonarQube’s Enterprise Edition supports COBOL, ABAP, PL/SQL, PL/I, RPG, and VB6 alongside modern languages. For organizations maintaining code across multiple decades of technology, SonarQube provides unified analysis.
Teams that prioritize the IDE feedback loop. SonarLint’s connected mode creates the tightest feedback loop between what developers see locally and what the CI pipeline enforces. Code Climate has no IDE integration. This shift-left advantage means SonarQube catches issues before code is even committed, while Code Climate only catches issues after a PR is opened.
Budget-conscious teams. SonarQube’s free Community Build and Cloud Free tier provide more analysis depth than Code Climate’s paid plans. A team can get started with SonarQube at zero cost and receive deeper analysis than they would get paying $15/user/month for Code Climate.
Teams that use Azure DevOps. SonarQube supports Azure DevOps with PR decoration and quality gate enforcement. Code Climate does not support Azure DevOps.
When to Choose Code Climate
Teams that want the absolute simplest setup. Code Climate’s zero-configuration cloud setup is genuinely the fastest path to getting maintainability feedback on pull requests. If setup simplicity is the top priority above all else, Code Climate delivers.
Teams that specifically value A-F maintainability grading. Code Climate’s letter-grade system is intuitive and easy to communicate to non-technical stakeholders. If your organization’s quality conversations center on maintainability grades and you do not need the broader analysis SonarQube provides, Code Climate’s approach may fit your workflow.
Open-source projects on a zero budget. Code Climate’s free tier for public repositories provides maintainability analysis and coverage tracking at no cost. However, SonarQube Cloud Free also covers open-source projects (and private projects up to 50K LOC), so this advantage is limited.
Code Climate is not ideal if: You need security scanning (Code Climate has none). You need self-hosted deployment (Code Climate is cloud-only). You need deep rule coverage beyond structural metrics. You want IDE integration. You need quality gate enforcement beyond basic PR checks. You need legacy language support. You use Azure DevOps. In most of these cases, SonarQube is the better choice.
Alternatives to Consider
If neither SonarQube nor Code Climate perfectly matches your requirements, several other tools are worth evaluating.
Codacy is the closest to an “all-in-one” platform. It provides code quality analysis, SAST, SCA, DAST (on Business plan), secrets detection, AI Guardrails, AI Reviewer, and coverage tracking at $15/user/month. For teams that want Code Climate’s simplicity but with security scanning and deeper analysis, Codacy is the most natural alternative. It supports 49 languages and offers pipeline-less setup similar to Code Climate.
DeepSource offers 5,000+ analysis rules with a sub-5% false positive rate – the highest signal-to-noise ratio in the category. Its five-dimension PR report cards and AI-powered Autofix are more advanced than both SonarQube’s and Code Climate’s approaches. For teams that want modern, AI-native static analysis with deep rule coverage, DeepSource is a strong contender at $12/user/month (Team plan).
Qlty was built by the Code Climate founding team and is the most natural successor for teams migrating from Code Climate. It provides maintainability grading similar to Code Climate but with deeper analysis through 70+ embedded plugins covering 40+ languages. The free CLI is available for commercial use, and the cloud platform starts at $15/contributor/month.
CodeRabbit is the best dedicated AI code review tool in 2026. If your primary gap is AI-powered PR feedback rather than static analysis or quality gates, CodeRabbit provides deeper contextual review than either SonarQube or Code Climate. It is best used alongside a code quality platform, not as a replacement.
Semgrep is the leading open-source SAST engine with over 10,000 community rules. If your primary concern is security scanning and you want to pair it with Code Climate for quality, Semgrep fills the security gap that Code Climate cannot cover. Semgrep Pro starts at $35/contributor/month.
Migration: Code Climate to SonarQube
When Migration Makes Sense
Most teams evaluating SonarQube vs Code Climate in 2026 are either starting fresh or considering migrating away from Code Climate. The most common motivations for migration include: wanting deeper analysis beyond maintainability metrics, needing security scanning without adding a separate vendor, requiring self-hosted deployment, wanting IDE integration through SonarLint, and concerns about Code Climate’s reduced investment following the Velocity sunset and the founding team’s departure to Qlty.
Migration Steps
Step 1: Start with SonarQube in parallel. Set up SonarQube Cloud Free or the Community Build and connect it to the same repositories you analyze with Code Climate. Run both tools for 2-4 weeks.
Step 2: Compare findings. SonarQube will almost certainly find more issues than Code Climate – including bugs, security vulnerabilities, and code patterns that Code Climate’s maintainability analysis does not cover. Evaluate whether the additional findings are relevant to your team.
Step 3: Map your quality standards. If you use Code Climate’s maintainability grades in your workflow, define equivalent conditions in SonarQube’s quality gates. For example, if you require a minimum B grade in Code Climate, set SonarQube quality gates for maximum complexity, duplication limits, and minimum coverage that approximate that standard.
Step 4: Migrate coverage reporting. Update your CI/CD pipeline to upload coverage reports to SonarQube instead of (or in addition to) Code Climate. SonarQube supports the same standard coverage formats.
Step 5: Switch PR checks. Update your GitHub/GitLab/Bitbucket branch protection rules to require SonarQube’s quality gate instead of Code Climate’s status checks. Monitor for any workflow disruptions.
Step 6: Decommission Code Climate. Once the team is comfortable with SonarQube’s workflow and all critical processes have been migrated, remove the Code Climate integration and cancel the subscription.
What You Gain
Moving from Code Climate to SonarQube gives you: 6,500+ rules versus Code Climate’s limited rule set, security scanning with OWASP/CWE coverage, quality gate enforcement that is genuinely best-in-class, SonarLint IDE integration with connected mode, technical debt quantified in remediation hours, support for 35+ languages, and self-hosted deployment option.
What You Lose
The migration trade-offs are minimal: Code Climate’s A-F maintainability grades do not have a direct equivalent in SonarQube (though SonarQube uses A-E quality ratings), and the initial setup requires more effort, especially for self-hosted deployment. Code Climate’s zero-configuration approach is simpler, but the simplicity comes at the cost of significantly shallower analysis.
Head-to-Head on Specific Scenarios
| Scenario |
Better Choice |
Why |
| Enforcing minimum code coverage on PRs |
SonarQube |
Quality gates with coverage conditions are best-in-class |
| Detecting security vulnerabilities |
SonarQube |
1,000+ security rules with taint analysis; Code Climate has none |
| Fastest possible setup |
Code Climate |
Zero-configuration cloud setup in minutes |
| Self-hosted deployment |
SonarQube |
Free Community Build; Code Climate is cloud-only |
| IDE-level feedback before commit |
SonarQube |
SonarLint connected mode; Code Climate has no IDE integration |
| Quantifying technical debt in hours |
SonarQube |
Remediation time estimates; Code Climate uses letter grades |
| Simple maintainability grading |
Code Climate |
A-F grades are intuitive and easy to communicate |
| Legacy language support (COBOL, ABAP) |
SonarQube |
Enterprise Edition uniquely supports legacy languages |
| Azure DevOps integration |
SonarQube |
Code Climate does not support Azure DevOps |
| Portfolio management across projects |
SonarQube |
Enterprise Edition aggregates metrics across all projects |
| AI-generated code governance |
SonarQube |
AI Code Assurance detects and verifies AI-generated code |
| Secrets detection in PRs |
SonarQube |
400+ secret patterns; Code Climate has no secrets detection |
| Budget-constrained team |
SonarQube |
Free Community Build and Cloud Free provide more than Code Climate’s paid plan |
| Compliance reporting (OWASP, CWE) |
SonarQube |
Enterprise security reports; Code Climate has no security reporting |
| Test coverage tracking |
Tie |
Both track coverage effectively |
Final Verdict
SonarQube and Code Climate are not in the same weight class in 2026. SonarQube is a comprehensive code quality and security platform with 6,500+ rules, enterprise quality gate enforcement, self-hosted deployment, AI features, and security scanning. Code Climate is a lightweight maintainability tool that assigns letter grades and tracks coverage. The comparison is between a full-featured platform and a single-purpose tool.
For teams of any size working in any language: SonarQube provides more value, often at lower cost. The free Community Build and Cloud Free tier deliver deeper analysis than Code Climate’s paid plans. The Developer Edition at $2,500/year provides security scanning, branch analysis, and SonarLint connected mode that Code Climate cannot match at any price. The quality gate enforcement, technical debt tracking, and IDE integration create a development workflow that catches issues earlier and enforces standards more effectively.
For teams currently using Code Climate: Evaluate SonarQube Cloud Free alongside your existing Code Climate setup. Run both tools on the same repositories for 2-4 weeks. In nearly every case, SonarQube will find more issues, provide better enforcement, and cost less. The migration is straightforward, and the benefits are substantial.
For teams that want more than what either tool provides: The strongest toolchain in 2026 pairs SonarQube (for deep quality analysis and security scanning) with CodeRabbit (for AI-powered PR review) and, if security requirements are stringent, a dedicated security scanner like Semgrep or Snyk Code. This layered approach provides coverage that no single platform can match.
Code Climate served the developer community well when it launched, and its A-F grading system was an elegant solution for making code quality accessible. But the market has evolved. SonarQube, Codacy, DeepSource, and Qlty (built by Code Climate’s own founding team) all provide deeper analysis, broader security coverage, and more mature enforcement mechanisms. For teams making a decision in 2026, SonarQube is the clear winner in this comparison – and it is not particularly close.
Frequently Asked Questions
Is SonarQube better than Code Climate?
SonarQube is better for teams that need deep deterministic rule coverage (6,500+ rules vs Code Climate’s smaller rule set), self-hosted deployment for data sovereignty, enterprise quality gate enforcement, compliance reporting aligned to OWASP/CWE/SANS standards, and support for legacy languages like COBOL and ABAP. Code Climate is better for teams that want fast cloud-based setup with zero infrastructure management, simple maintainability grading (A-F scores), and lightweight PR feedback without operational overhead. For most teams evaluating code quality platforms in 2026, SonarQube provides substantially more value per dollar – especially since the Community Build is free.
Is Code Climate free?
Code Climate Quality is free for public open-source repositories. For private repositories, paid plans start at approximately $15/user/month. The free tier only covers open-source projects and does not include private repository scanning. By comparison, SonarQube offers a free Community Build for self-hosted deployment (unlimited private repos, 20+ languages) and a Cloud Free tier that supports up to 50,000 lines of code with branch and PR analysis at no cost. SonarQube’s free options are significantly more useful for teams with private codebases.
Is SonarQube free to use?
Yes, SonarQube offers two free options. The Community Build is a fully free, open-source, self-hosted edition supporting 20+ languages with basic quality gates (but no branch or PR analysis). SonarQube Cloud Free supports up to 50,000 lines of code with branch analysis, PR decoration, and 30 language support at no cost. Paid editions start at approximately $2,500/year for the Developer Edition (self-hosted) or EUR 30/month for Cloud Team. Both free tiers provide substantially more functionality than Code Climate’s free offering.
Can SonarQube be self-hosted?
Yes, self-hosted deployment is one of SonarQube’s core strengths and a major differentiator from Code Climate. The free Community Build can be deployed on your own infrastructure with PostgreSQL as the database backend. Commercial editions (Developer, Enterprise, Data Center) add features while maintaining the self-hosted model. The Data Center Edition provides high availability with horizontal scaling. Code Climate does not offer any self-hosted deployment option – it is entirely cloud-based.
Does Code Climate support self-hosted deployment?
No, Code Climate is a cloud-only platform with no self-hosted deployment option. All code analysis runs on Code Climate’s cloud infrastructure. Organizations with data sovereignty requirements, air-gapped environments, or compliance mandates that prohibit sending code to third-party cloud services cannot use Code Climate. SonarQube is the clear choice for these organizations, offering free self-hosted deployment through the Community Build and commercial self-hosted editions.
How much does SonarQube cost compared to Code Climate?
SonarQube’s free Community Build provides self-hosted analysis at zero cost, and the Cloud Free tier covers up to 50K lines of code. Paid editions start at EUR 30/month for Cloud Team or approximately $2,500/year for the Developer Edition (self-hosted). Code Climate starts at approximately $15/user/month for private repositories. For a 10-developer team, Code Climate costs roughly $1,800/year while SonarQube Cloud Free or Community Build costs nothing. Even paid SonarQube (Developer Edition at $2,500/year) provides significantly deeper analysis than Code Climate at a similar price point.
Which tool has better quality gates?
SonarQube has substantially better quality gate enforcement. SonarQube allows you to define conditions that block PR merges based on minimum code coverage, maximum new bugs, duplication limits, security vulnerability severity, and technical debt ratio. These gates integrate with GitHub, GitLab, Bitbucket, and Azure DevOps branch protection rules. Code Climate provides basic PR status checks for maintainability and coverage thresholds, but the sophistication and granularity of its enforcement does not match SonarQube’s. For teams that rely on automated quality enforcement to maintain standards, SonarQube’s gates are best-in-class.
Which tool has better language support?
SonarQube supports 35+ languages in commercial editions (20+ in the free Community Build), including legacy enterprise languages like COBOL, ABAP, PL/SQL, PL/I, RPG, and VB6 in the Enterprise Edition. The analysis depth per language is exceptional – Java alone has 900+ rules. Code Climate supports approximately 30 languages through its embedded analysis engines. While the raw language count is comparable, SonarQube’s per-language analysis depth is significantly greater, with thousands more language-specific rules covering bugs, vulnerabilities, and complex code patterns that Code Climate does not detect.
Can I use SonarQube and Code Climate together?
You can run both tools on the same repositories, but there is limited practical value in doing so. The overlap in code quality analysis is significant – both tools detect maintainability issues, complexity problems, and duplication. SonarQube provides deeper analysis across every dimension that Code Climate covers. If your goal is to complement SonarQube’s quality analysis, pairing it with a security-focused tool like Semgrep or Snyk, or an AI-powered reviewer like CodeRabbit, is more effective than adding Code Climate on top.
Is Code Climate still maintained in 2026?
Code Climate Quality is still an active product and continues to provide maintainability analysis, test coverage tracking, and code quality grading. However, Code Climate Velocity – the engineering metrics product that tracked DORA metrics and team productivity – was sunset. The founding team moved on to build Qlty, a new code quality platform. Many teams are evaluating alternatives due to the reduced investment in the Quality product, the loss of Velocity, and the availability of more modern tools like SonarQube, Codacy, and DeepSource that offer deeper analysis and security scanning.
What happened to Code Climate Velocity?
Code Climate Velocity – the engineering metrics product that tracked DORA metrics, cycle time, deployment frequency, and team throughput – was sunset. Teams that relied on Velocity for engineering performance tracking need a separate replacement. LinearB is the most direct successor for DORA metrics and workflow automation. The loss of Velocity significantly narrowed Code Climate’s value proposition, as many organizations subscribed to Code Climate primarily for the combination of Quality and Velocity. The Quality product alone faces stiff competition from tools like SonarQube that offer deeper analysis at lower cost.
Which is easier to set up, SonarQube or Code Climate?
Code Climate is easier to set up. Connect your GitHub account, select repositories, and analysis begins within minutes. There is no infrastructure to manage. SonarQube Cloud is similarly straightforward but requires adding a SonarScanner to your CI/CD pipeline. Self-hosted SonarQube Server requires provisioning a database (PostgreSQL), deploying the server, configuring authentication, and installing the scanner – typically a full day of DevOps effort. However, SonarQube Cloud Free provides a managed experience that is nearly as fast to set up as Code Climate, with significantly deeper analysis.
Does SonarQube have security scanning?
Yes, SonarQube includes substantial security scanning capabilities. Approximately 15% of its 6,500+ rules are security-focused, covering OWASP Top 10, CWE Top 25, and SANS Top 25 vulnerability categories. The Developer Edition and above include taint analysis for detecting injection vulnerabilities across multiple files. The Enterprise Edition offers security compliance reports and the Advanced Security add-on provides SCA (dependency scanning), SBOM generation, and malicious package detection. Code Climate does not include any security scanning – it focuses exclusively on maintainability and coverage.
Should I migrate from Code Climate to SonarQube?
For most teams, migrating from Code Climate to SonarQube is a significant upgrade. SonarQube provides deeper analysis (6,500+ rules vs Code Climate’s smaller set), better quality gate enforcement, security scanning, technical debt quantification in remediation hours, and a free self-hosted option. The main trade-off is increased setup complexity for self-hosted deployments – but SonarQube Cloud eliminates that. Run both tools in parallel for 2-4 weeks before migrating to compare findings. Most teams find that SonarQube catches everything Code Climate catches plus significantly more, making the migration straightforward to justify.
Originally published at aicodereview.cc





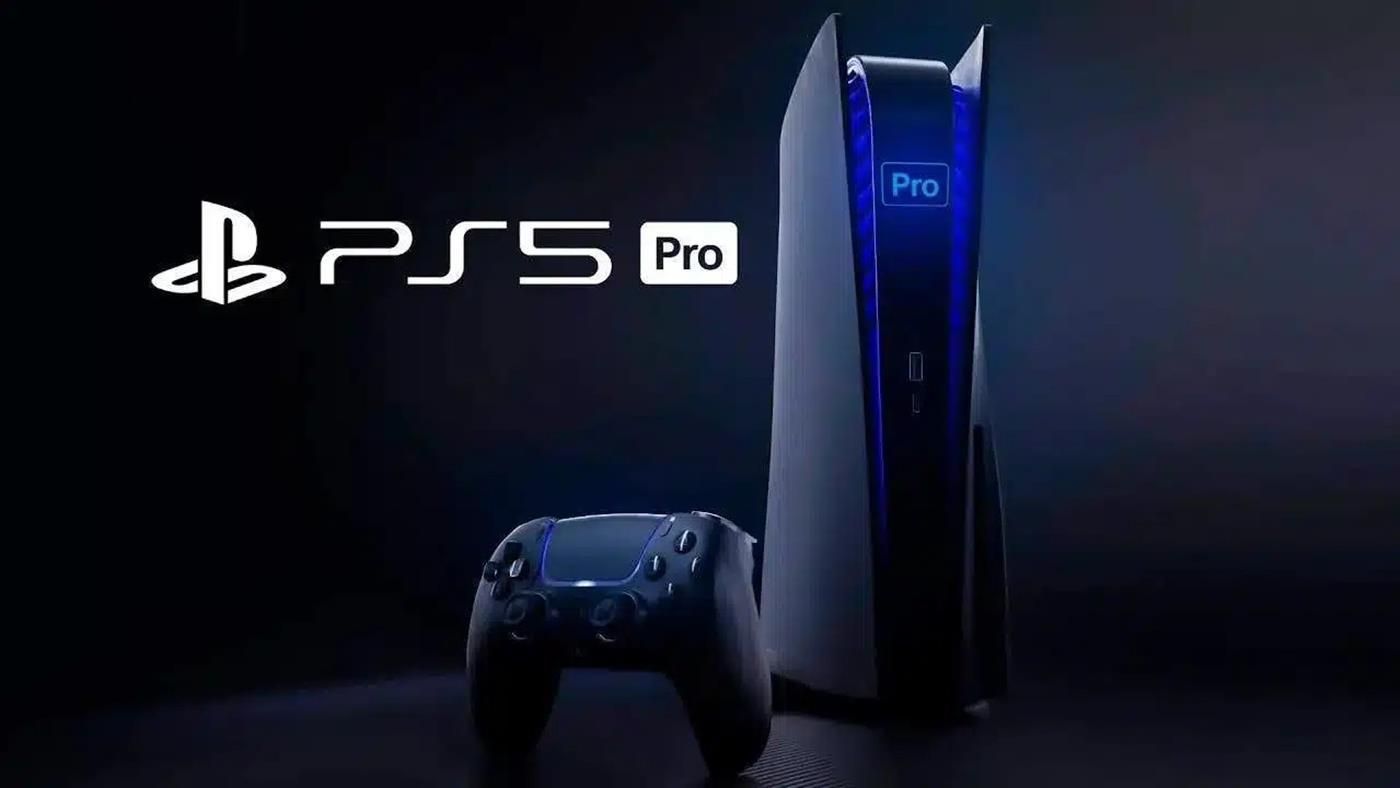
 PS5 fiyatlarına yeni bir zam daha gelebilir. Sızıntılara göre PS5 Slim, PS5 Pro ve PlayStation Portal için Avrupa fiyatlarında ciddi artışlar gündemde. İşte detaylar…